

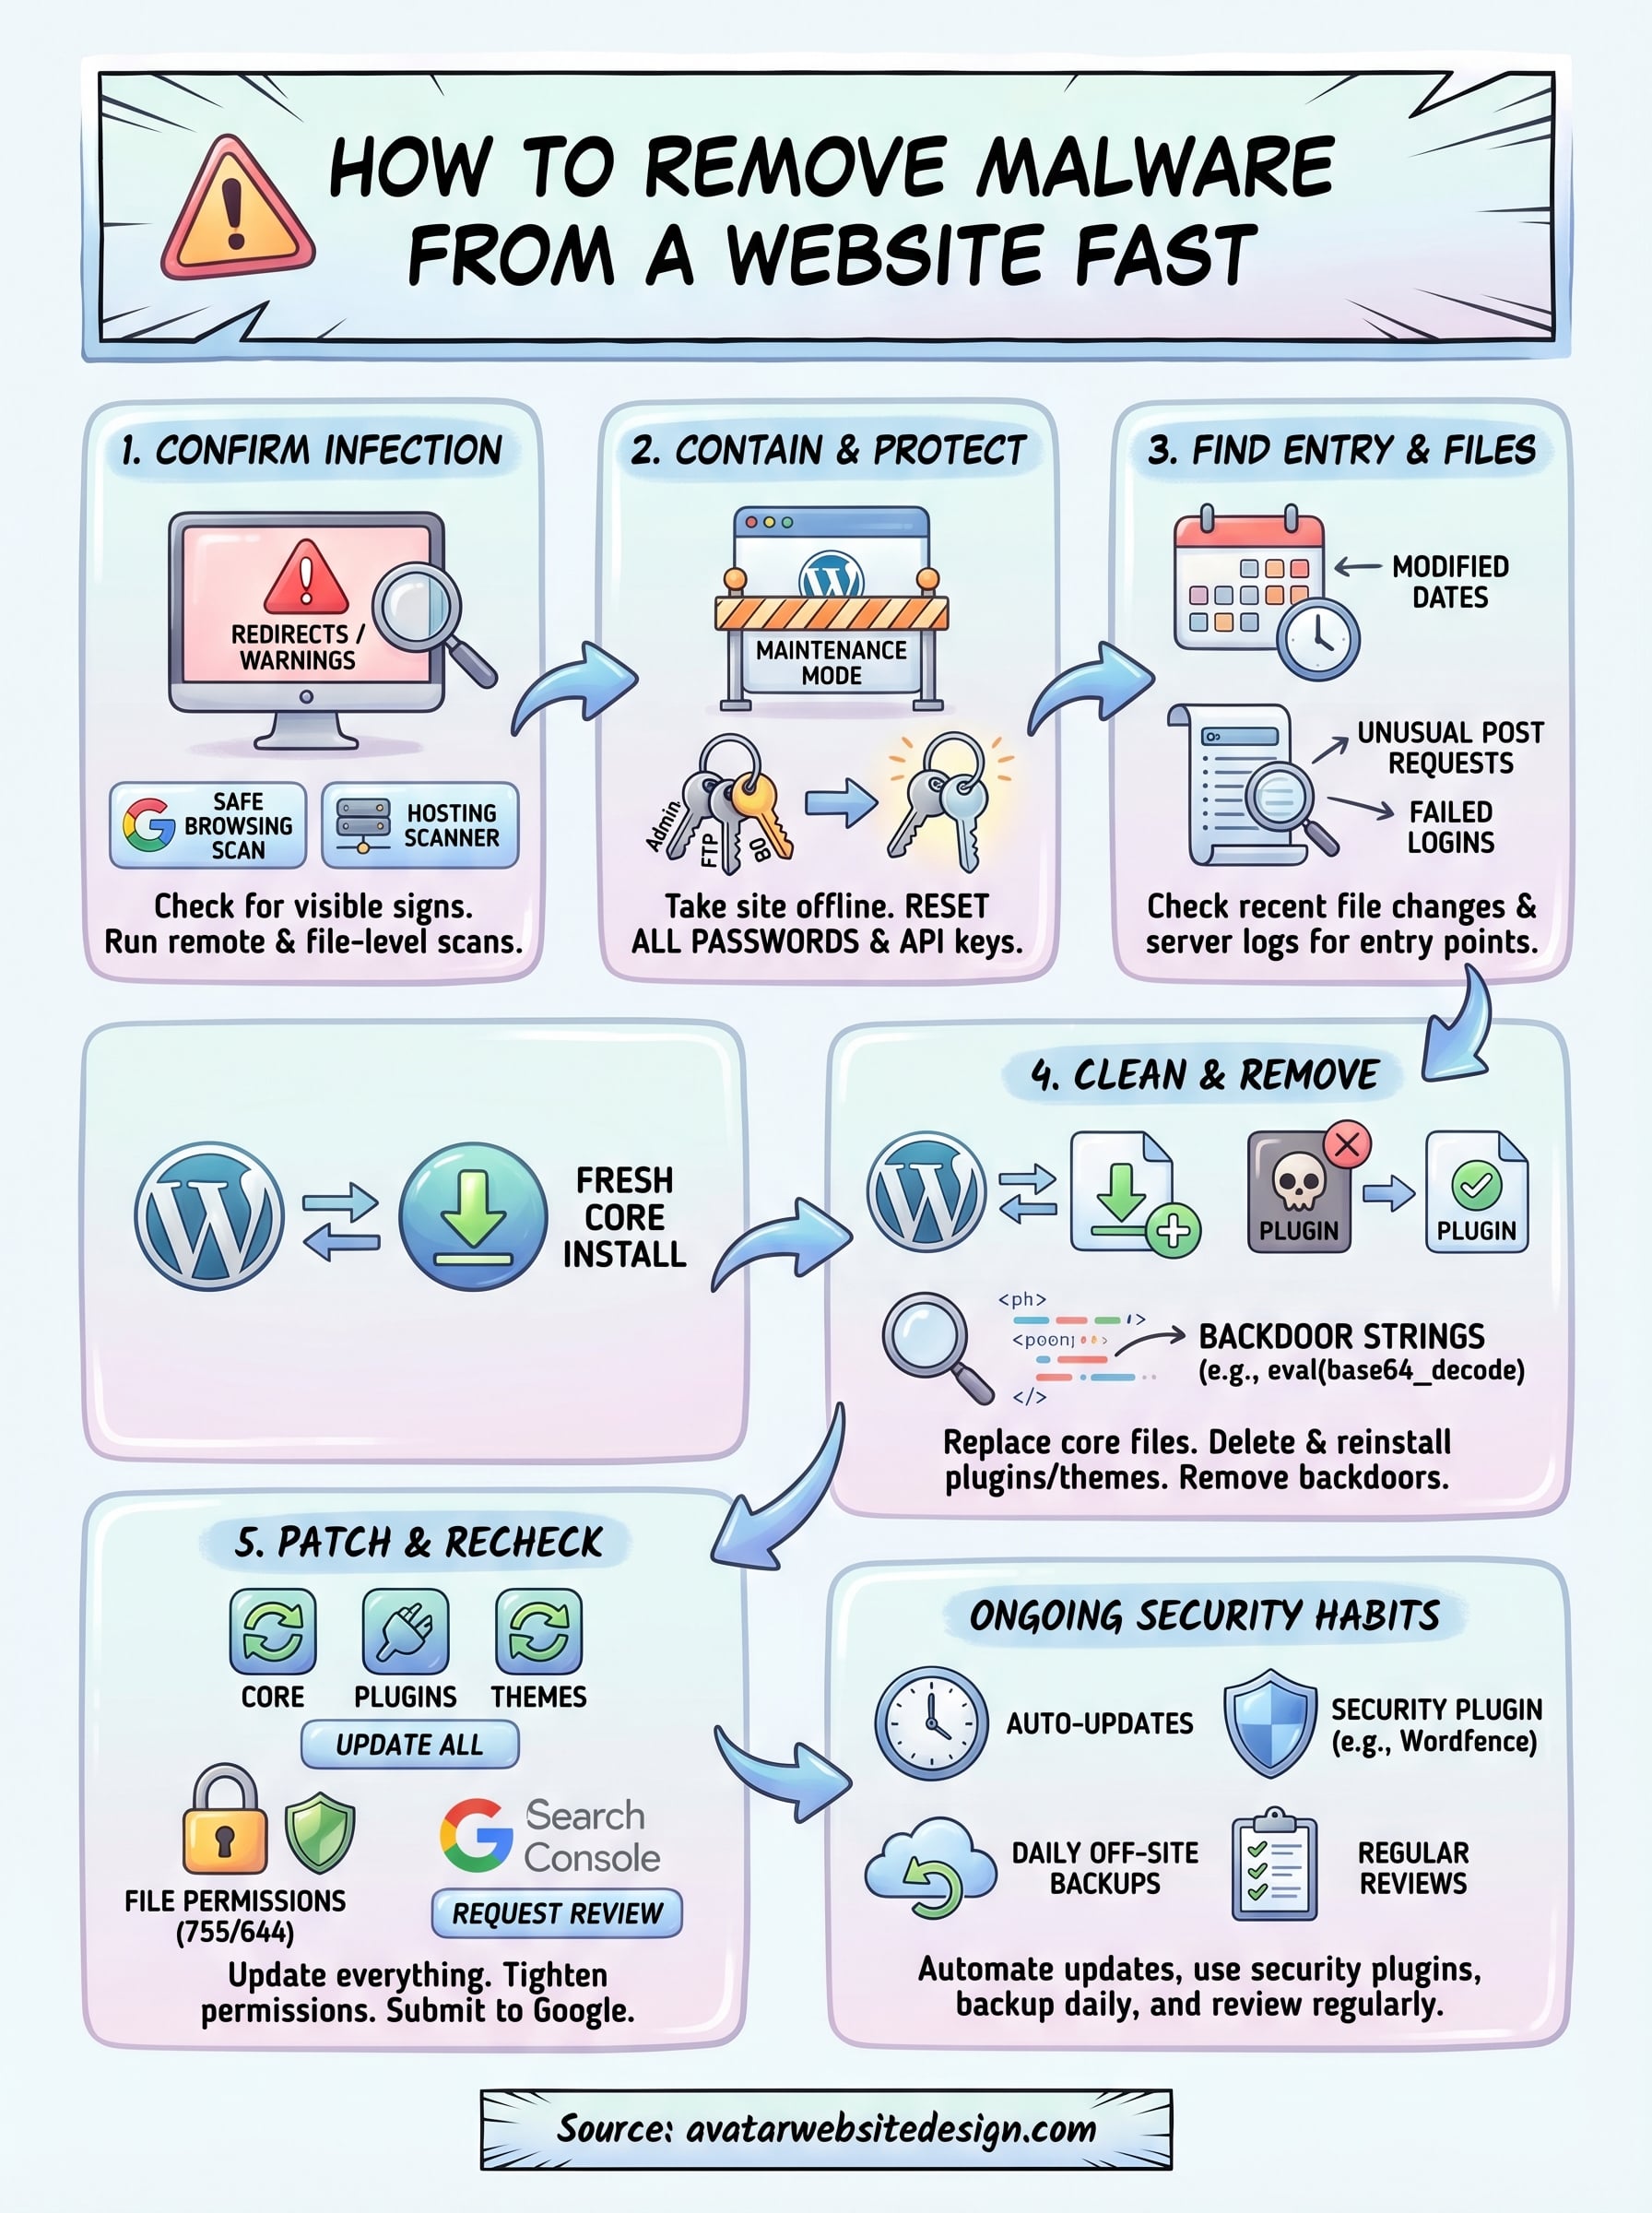
You check your website one morning and something’s off. Maybe Google is flagging it with a red warning screen. Maybe customers are telling you the site redirects to something sketchy. Either way, the sinking feeling is the same, your site has been compromised, and you need to know how to remove malware from a website before it costs you traffic, trust, and revenue.
Malware infections hit small business websites harder than most people realize. A single compromised plugin or outdated script can open the door to injected code, stolen customer data, and search engine blacklisting. The longer it sits, the worse the damage gets.
At Avatar Website Design, we build and maintain websites for small businesses, and that includes helping owners deal with security threats like these. This guide walks you through the exact steps to identify, remove, and recover from a malware infection on your site. Whether you plan to handle it yourself or bring in professional help, you’ll have a clear action plan by the end.
Before you start: confirm the infection
Jumping straight into cleanup without knowing what you are dealing with wastes time and risks missing hidden threats. Before learning how to remove malware from a website, you need to confirm an infection exists and understand what type you are working with. That information shapes every step that follows.
Signs your site is infected
Your site usually gives you visible warning signals before any scan confirms the actual problem. Watch for these:
- Google Search Console shows a "Security Issues" alert in the Security and Manual Actions panel
- Visitors report being redirected to unrelated or suspicious websites
- Your hosting provider suspends your account due to malicious activity
- Antivirus software flags your domain
- Unfamiliar admin accounts or files appear without explanation
- Pages display content you never created or published
Check Google Search Console first, since Google often detects infections before site owners do.
If Google has already blacklisted your site, you need to fix the malware and then submit a review request through Search Console. Skipping the review request means the warning stays up even after you finish the cleanup.
How to scan before you clean
Run a remote scan on your site’s URL using Google Safe Browsing to check for known threats at no cost. This gives you a quick public-facing picture of what Google has already flagged. For a deeper file-level scan, log into your hosting control panel and use the built-in malware scanner if your host provides one. Most managed WordPress hosts include this as a standard feature.
Comparing results from both tools gives you a clearer picture of what you are dealing with before you touch a single file.
Step 1. Contain the damage and protect accounts
Once you confirm an infection, your first priority is stopping the spread. Knowing how to remove malware from a website means nothing if your accounts stay open to the attacker who placed it there in the first place. Contain the damage first, then clean.
Take your site offline temporarily
Putting your site into maintenance mode limits exposure to your visitors while you work. Log into your hosting control panel and either activate a maintenance page or temporarily suspend the site. This prevents infected pages from loading for anyone who visits during cleanup.
Do not skip this step if your site is actively redirecting visitors or serving malicious downloads. Every minute it stays live, you risk harming your audience and worsening the damage to your search rankings.
Change credentials across every account
Reset every password tied to your site immediately. That includes your WordPress admin account, hosting control panel, FTP account, and database. Use a strong, unique password for each one.
Here is a quick checklist of accounts to lock down:
- WordPress admin users (delete any unfamiliar ones)
- Hosting control panel login
- FTP and SFTP accounts
- Database user credentials
- Email accounts connected to the domain
Revoke active API keys and access tokens your site uses, then generate fresh ones after the cleanup is complete.
Step 2. Find the entry point and infected files
Cleaning infected files without finding where the attacker entered is like patching a window while the front door stays open. To properly understand how to remove malware from a website, you need to trace both the infection source and every file it touched before you start deleting anything.
Check your file modification dates
Your hosting control panel or an FTP client shows file modification timestamps for every file on your server. Sort your core files by "last modified" date and look for anything changed around the time the infection first appeared. On a WordPress site, suspicious changes in wp-config.php, the wp-content folder, or .htaccess are the most common red flags worth examining first.
If you find injected code in .htaccess, it often looks like a block of encoded characters or unfamiliar redirect rules inserted at the very top of the file.
Trace how the attacker got in
Review your server access logs through your hosting control panel to spot unusual POST requests, unknown IP addresses, or repeated failed login attempts near the infection date. The most common entry points are outdated plugins, nulled themes, weak admin passwords, and exposed file upload forms. Pinpointing the exact entry point tells you precisely what needs patching once the cleanup is complete.
Step 3. Clean the site and remove backdoors
With the infected files identified, you are ready to start removing the malicious code. This is the most hands-on part of learning how to remove malware from a website, and doing it thoroughly means you check every flagged file before moving forward.
Replace core files with clean versions
Download a fresh copy of WordPress directly from WordPress.org and replace your core files, specifically the wp-admin and wp-includes folders, with clean versions. Do not touch the wp-content folder yet since that is where your themes and plugins live. For each infected plugin or theme, delete it completely and reinstall from the official source rather than trying to manually edit individual lines of malicious code.
Editing malicious code line by line leaves room for human error. Replacing files entirely with clean, verified versions is faster and more reliable.
Find and remove backdoors
Attackers frequently plant backdoor files in writable directories so they can regain access even after a cleanup. Look for PHP files in your uploads folder, which should never contain executable code. Search your files for common backdoor functions using your hosting file manager’s search tool, then delete any file containing them. Common strings to search for include:
eval(base64_decodesystem(exec(passthru(
Step 4. Patch, harden, and request rechecks
Removing infected files solves today’s problem but not tomorrow’s. The final stage of knowing how to remove malware from a website is closing the gaps that let the attacker in and notifying search engines that your site is clean.
Update everything and lock down your site
Start by updating WordPress core, every plugin, and every theme to the latest stable version. Delete any plugins or themes you are not actively using, since inactive code is still a valid entry point for attackers. After updating, tighten your site’s file permissions so attackers cannot write to directories they have no business accessing.
Set folder permissions to 755 and file permissions to 644 as a baseline. Your wp-config.php file should be set to 600.
Submit a reconsideration request to Google
Once your site is clean and hardened, log into Google Search Console and navigate to the Security Issues report. Click "Request a Review" and briefly describe what you did to remove the malware and prevent reinfection. Be specific. Google typically responds within a few days, and once the review passes, the Safe Browsing warning comes down automatically. Skipping this step leaves the warning active even on a fully clean site, which continues to hurt your traffic and credibility.
Keep it secure going forward
One cleanup is not a permanent fix. Knowing how to remove malware from a website gets you back online, but ongoing security habits are what keep you from repeating this process. Set your WordPress core, plugins, and themes to update automatically, or check for updates at least once a week. Install a security plugin like Wordfence or Solid Security to monitor file changes, block brute-force login attempts, and alert you the moment something unusual happens.
Back up your site daily using a plugin like UpdraftPlus, and store those backups somewhere off your server, such as Google Drive or Dropbox. A clean, recent backup is your fastest recovery option if an attacker gets through again. You should also schedule a monthly review of your admin users, active plugins, and file permissions to catch anything suspicious before it becomes a full infection.
If managing all of this feels like too much on top of running your business, Avatar Website Design’s website maintenance plans handle it for you.