

A single security breach can cost a small business everything, customer trust, revenue, and years of hard work building a reputation. Cybercriminals don’t just target large corporations. They actively hunt for vulnerable small business websites because they’re often easier to exploit. If you’re wondering how to secure a website, you’re already taking the right first step. The threat is real: 43% of cyberattacks target small businesses, and many of those businesses never fully recover.
Your website is more than a digital storefront. It holds customer data, processes transactions, and represents your brand 24/7. Without proper security measures, you’re leaving the door wide open for hackers, malware, and data thieves. The good news? Protecting your site doesn’t require a massive budget or a degree in cybersecurity. It requires the right knowledge and consistent action.
At Avatar Website Design, we build and maintain websites for small businesses every day. We’ve seen what happens when security gets overlooked, and we’ve helped clients recover from preventable attacks. That experience shaped this guide. Below, you’ll find a 15-step checklist covering SSL certificates, software updates, password policies, firewalls, and security plugins. Each step is practical and actionable, designed specifically for business owners who want to protect their investment without getting lost in technical jargon.
Before you start: map your risks and site setup
You can’t protect what you don’t understand. Before implementing any security measures, you need a clear picture of what you’re protecting and where your vulnerabilities lie. Most small business owners skip this step and jump straight to installing plugins or changing passwords. That approach wastes time and leaves critical gaps in your defense. Understanding how to secure a website begins with mapping your unique risk profile and technical environment.
Your website isn’t a generic target. Different sites face different threats based on what they do and how they’re built. An e-commerce site handling credit cards faces different risks than a simple brochure site with a contact form. A WordPress site with 20 plugins has a larger attack surface than a static HTML site. Taking 30 minutes to document your setup will guide every security decision you make in the steps ahead.
Identify what you’re protecting
Start by listing every type of sensitive information your website collects or stores. Customer names, email addresses, phone numbers, payment data, login credentials, business records, these all require protection. If your site processes transactions, you’re handling financial information that criminals actively target. If you collect personal data through forms, you’re responsible for keeping that information secure and private.
Next, identify critical functions that must remain available. Can customers place orders? Do you rely on appointment booking? Is there a member login area? Understanding what would hurt your business most if it went offline helps you prioritize your security efforts. A site that generates revenue directly needs stronger uptime protection than a simple informational site.
"The best security strategy starts with knowing exactly what you’re defending and what the consequences of failure would be."
Document your current technology stack
Create a simple inventory of every technology component your website uses. Write down your content management system (WordPress, Shopify, custom code), your hosting provider, your domain registrar, and any third-party services integrated into your site. List every plugin, theme, or extension you’ve installed. Include version numbers for your CMS and any software components you can identify.
This inventory serves multiple purposes. First, it shows you how many potential entry points exist for attackers. Each plugin, theme, and integration represents a potential vulnerability. Second, it helps you track what needs updating when security patches release. Third, it reveals unnecessary components you can remove to reduce your attack surface.
Keep this document updated as you add or remove components. Store it somewhere secure but accessible, you’ll reference it regularly as you maintain your site’s security.
Assess your biggest vulnerabilities
Small business websites typically share common weak points that attackers exploit first. Outdated software ranks at the top. If your WordPress installation, plugins, or themes haven’t been updated in months, you’re running known vulnerabilities that hackers can exploit using automated tools. Default admin usernames like "admin" or "administrator" make brute-force attacks significantly easier.
Look at your current password practices honestly. Do you use the same password across multiple accounts? Are your passwords short or based on dictionary words? Do team members share login credentials? Each of these practices creates an easy entry point. Check whether your site currently uses HTTPS across all pages. If you’re still running HTTP, all data transmitted between your site and visitors travels in plain text.
Evaluate your backup situation right now. When was the last backup created? Where is it stored? Could you restore your site if it disappeared tomorrow? Many small businesses don’t realize they have no working backups until disaster strikes. Finally, consider whether you have any visibility into who’s accessing your site’s admin area and what they’re doing once logged in.
Write down the specific vulnerabilities you identify in your site. These become your priority list for the security steps ahead.
Steps 1–3: Secure your domain, hosting, and HTTPS
Your foundation matters. Domain control, reliable hosting, and HTTPS encryption form the base layer of website security. Attackers often target these foundational elements first because compromising them gives complete control over your site. If someone hijacks your domain, they can redirect your traffic anywhere. If your hosting lacks basic protections, malware spreads easily. Without HTTPS, every piece of data traveling between your site and visitors can be intercepted and read by anyone watching the connection.
These first three steps in how to secure a website address your infrastructure. They require upfront effort but provide lasting protection that doesn’t need constant maintenance. You’ll configure these once properly and then perform occasional reviews to verify they’re still working correctly.
Step 1: Lock down your domain registration
Log into your domain registrar account right now and enable domain lock (also called domain transfer lock or registrar lock). This feature prevents unauthorized transfers of your domain to another registrar. Without it, an attacker who gains access to your registrar account can steal your domain in minutes. Find this setting in your domain management panel and turn it on immediately.
Enable two-factor authentication (2FA) on your domain registrar account. Use an authenticator app like Google Authenticator or Microsoft Authenticator rather than SMS text messages, which can be intercepted. Set up registry lock if your registrar offers it. This adds an extra layer that requires manual verification before any changes to your domain settings take effect.
Update your domain contact information to use a private email address you monitor regularly. Many domain hijackings succeed because attackers request password resets to outdated email addresses the owner no longer checks. Review your WHOIS privacy settings to protect your personal contact information from public view while ensuring you receive important notifications about your domain.
"Domain control is website control. Protecting your domain registration is the single most important security decision you’ll make."
Step 2: Choose security-focused hosting
Your hosting provider serves as your site’s security partner. Shared hosting plans that cost $5 per month rarely include the security features small businesses need. Look for hosts that offer server-level firewalls, regular security monitoring, automatic malware scanning, and free SSL certificates. These features should be standard, not paid add-ons.
Verify your hosting includes automatic daily backups stored on separate infrastructure from your live site. Ask your host about their backup retention period and test the restore process at least once. Ensure your hosting plan provides adequate resources (bandwidth, storage, processing power) because performance issues often force sites to disable security features just to stay functional.
Step 3: Install and configure SSL/HTTPS properly
Purchase and install an SSL certificate on your domain if you haven’t already. Most hosting providers now include free SSL certificates through Let’s Encrypt. Navigate to your hosting control panel, find the SSL section, and activate SSL for your domain. The certificate encrypts all data transmitted between your server and visitors’ browsers.
Installing the certificate is only half the job. You must force all traffic to use HTTPS by implementing redirects. Add this code to your .htaccess file if you run an Apache server:
RewriteEngine On
RewriteCond %{HTTPS} off
RewriteRule ^(.*)$ https://%{HTTP_HOST}%{REQUEST_URI} [L,R=301]
Update your website configuration to reference HTTPS URLs in all internal links. Change your canonical URLs and XML sitemap to use HTTPS. Test every page on your site to verify the padlock icon appears in the browser address bar without warnings about mixed content.
Steps 4–6: Patch fast and reduce your attack surface
Outdated software is the number one entry point for automated attacks on small business websites. Hackers scan thousands of sites daily looking for known vulnerabilities in outdated platforms, plugins, and themes. When developers discover security flaws and release patches, that information becomes public knowledge. Attackers immediately begin exploiting sites that haven’t updated. The window between patch release and active exploitation often measures in hours, not days.
Reducing your attack surface means eliminating unnecessary components that could become vulnerabilities. Every plugin, theme, user account, and feature you don’t actively use represents a potential entry point. Understanding how to secure a website means accepting that less is more. The fewer components you run, the fewer things can break or get exploited.
Step 4: Update everything immediately
Check for updates at least weekly. Log into your website’s admin panel and navigate to the updates section. Apply all available updates for your core platform (WordPress, Joomla, Drupal, etc.), every active plugin, and your current theme. Don’t skip updates because you’re worried about breaking your site. Outdated software will get exploited, breaking is a possibility, exploitation is a certainty.
Enable automatic updates for minor security releases if your platform supports it. WordPress allows automatic updates for core minor versions and plugins. Configure your settings to apply these updates immediately when they release. For major version updates, test on a staging environment first, then apply to your live site within 48 hours.
Your hosting control panel likely needs updates too. Check for PHP version updates, database updates, and server software patches. Many hosts allow you to upgrade your PHP version through their control panel. Run the most recent stable PHP version your site supports. Older PHP versions contain known security vulnerabilities that attackers actively exploit.
"Every day you delay a security update is another day attackers have to find and exploit your site."
Step 5: Remove unused plugins, themes, and features
Audit every plugin and theme installed on your site. Delete completely any plugin you haven’t used in 90 days. Don’t just deactivate it. Inactive plugins still contain code that hackers can exploit. Remove all themes except your active theme and one backup theme. Multiple unused themes create unnecessary risk.
Review your user accounts and delete anyone who no longer needs access. Former employees, old contractors, and test accounts you created months ago all represent security risks. Each login credential is a potential point of compromise.
Disable features you don’t use. Turn off XML-RPC if you don’t need remote publishing capabilities. Disable pingbacks and trackbacks if you don’t use them. Remove contact forms from pages where you don’t need them. Every feature you disable reduces the code attackers can target.
Step 6: Disable file editing and directory browsing
Add this code to your wp-config.php file (for WordPress sites) to disable the built-in file editor:
define('DISALLOW_FILE_EDIT', true);
This prevents attackers who gain admin access from modifying your theme or plugin files directly through the dashboard. They’ll need FTP or SSH access to make changes, which represents a much higher barrier.
Prevent directory browsing by adding this to your .htaccess file:
Options -Indexes
Directory browsing allows anyone to view the contents of folders on your server that don’t contain index files. Attackers use this to discover file structures, find configuration files, and identify vulnerabilities. Disabling it removes this reconnaissance capability.
Steps 7–9: Lock down logins and admin access
Weak authentication is the easiest way for attackers to walk through your front door. Brute-force attacks hammer login pages thousands of times per hour, trying common username and password combinations until something works. Once inside your admin area, attackers can inject malware, steal data, or destroy your entire site. Strengthening how to secure a website requires fortifying every aspect of authentication and access control.
Most small business owners underestimate how aggressively automated bots target login pages. Your WordPress site receives login attempts every single day, whether you notice them or not. The difference between a secure site and a compromised one often comes down to these three authentication steps.
Step 7: Implement strong password policies
Require every user on your site to use passwords at least 16 characters long containing uppercase letters, lowercase letters, numbers, and symbols. Use a password manager like 1Password or Bitwarden to generate and store complex passwords. Never reuse passwords across different sites or services.
Change your admin username immediately if it’s "admin," "administrator," or your business name. Attackers try these default usernames first. Create a new admin account with an unpredictable username, then delete the old default account. Use completely different usernames for different team members rather than shared credentials.
Install a plugin that enforces password requirements and expires passwords every 90 days. Set failed login attempt limits to lock accounts after five wrong password tries. Configure account lockout duration for at least 30 minutes to slow down brute-force attacks.
"A strong password policy stops 95% of automated attacks before they even begin."
Step 8: Enable two-factor authentication
Add a two-factor authentication (2FA) plugin to your site immediately. This requires a second verification method beyond just the password. When you log in, you’ll enter your password and then provide a time-based code from an authenticator app on your phone.
Use authenticator apps like Google Authenticator or Microsoft Authenticator rather than SMS text messages for your second factor. Configure 2FA for every admin and editor account on your site. Generate backup codes and store them securely in case you lose access to your phone.
Step 9: Restrict admin access and monitor logins
Change your admin URL from the default /wp-admin or /admin to something unique. Use a security plugin to customize this path. Limit admin access by IP address if your team works from consistent locations. Add this code to your .htaccess file to whitelist specific IP addresses:
<Files wp-login.php>
order deny,allow
Deny from all
Allow from 203.0.113.0
Allow from 198.51.100.0
</Files>
Enable login activity logging to track every access attempt. Review these logs weekly for suspicious patterns like failed login attempts from foreign countries or login attempts during unusual hours. Immediately investigate any successful logins you don’t recognize.
Steps 10–12: Secure forms, data, and common attacks
Forms collect information, and attackers exploit them. Contact forms, login fields, search boxes, and payment processors all accept user input, which creates opportunities for malicious code injection. Hackers use automated scripts to test thousands of forms daily, looking for sites that trust user input without validation. Understanding how to secure a website means treating every piece of data users submit as potentially dangerous until you’ve verified and cleaned it. These three steps protect both your site and your customers’ sensitive information.
Step 10: Validate and sanitize all form inputs
Add server-side validation to every form on your site. Client-side validation (JavaScript checking) helps user experience but provides zero security because attackers bypass it easily. Your server must verify that email fields contain valid email formats, phone numbers match expected patterns, and text fields don’t contain executable code.
Implement input sanitization by stripping HTML tags and special characters from user submissions. Use your platform’s built-in sanitization functions. For WordPress sites, wrap all user input with sanitization functions like this:
$clean_email = sanitize_email($_POST['email']);
$clean_text = sanitize_text_field($_POST['message']);
Add CAPTCHA or reCAPTCHA to forms that don’t require user authentication. This blocks automated bot submissions that flood your forms with spam or probe for vulnerabilities. Limit file upload sizes and restrict allowed file types to specific formats you actually need.
Step 11: Encrypt sensitive data and minimize storage
Never store credit card numbers, social security numbers, or passwords in plain text on your database. Use your platform’s built-in encryption functions or rely on third-party payment processors that handle sensitive data for you. PayPal, Stripe, and similar services remove the burden of storing payment information entirely.
Hash all passwords using bcrypt or Argon2 algorithms before storing them. Configure your database connection to use SSL/TLS encryption. Add this line to your wp-config.php file to force encrypted database connections:
define('MYSQL_CLIENT_FLAGS', MYSQLI_CLIENT_SSL);
"The best way to protect customer data is to not store it in the first place. Only keep what you absolutely need."
Delete customer information you no longer need. Keep data for the minimum time required for business operations or legal compliance, then purge it completely from your system.
Step 12: Implement protection against injection attacks
Install a web application firewall (WAF) like Cloudflare or Sucuri to filter malicious traffic before it reaches your site. These services block SQL injection attempts, cross-site scripting (XSS), and cross-site request forgery (CSRF) attacks automatically. Most quality security plugins include built-in WAF features.
Use prepared statements for all database queries to prevent SQL injection. Never concatenate user input directly into SQL queries. Add CSRF tokens to forms that modify data. WordPress generates these automatically using nonce functions:
wp_nonce_field('form_action', 'form_nonce');
Verify the nonce when processing the form to confirm the request came from your site.
Steps 13–15: Monitor, back up, and recover quickly
Prevention stops most attacks, but detection and recovery determine whether a breach becomes a minor inconvenience or a business-ending disaster. Hackers who breach your defenses often work silently for days or weeks before you notice anything wrong. They plant backdoors, inject malware into old blog posts, or slowly siphon customer data. Knowing how to secure a website includes building systems that alert you immediately when something goes wrong and restore your site quickly when attacks succeed.
These final three steps create your safety net. Active monitoring catches problems early when they’re easy to fix. Regular backups ensure you can recover from any disaster. A tested recovery plan means you’ll restore your site in hours, not days.
Step 13: Set up active security monitoring
Install uptime monitoring that checks your site every 5 minutes and alerts you immediately if it goes down. Services like UptimeRobot or StatusCake send notifications via email, SMS, or app push notifications when your site becomes unreachable. Configure alerts for HTTP errors, slow response times, and SSL certificate expiration dates.
Enable file integrity monitoring through your security plugin to detect unauthorized changes to core files. This feature compares your current files against clean versions and alerts you when hackers modify critical system files. Set up malware scanning to run automatically every 24 hours and email you detailed reports.
Monitor your server logs weekly for suspicious patterns. Look for repeated failed login attempts from the same IP addresses, unusual traffic spikes during off-hours, or requests for files that don’t exist on your site. These patterns often indicate reconnaissance activities that precede attacks. Review your security plugin’s activity logs to track admin logins, plugin installations, and configuration changes.
"Catching an attack in progress gives you the chance to stop it before significant damage occurs."
Step 14: Create and test backup systems
Configure automated daily backups that run at the same time every night when traffic is lowest. Your backup must include your complete database, all website files, and your configuration files. Store backups in at least two separate locations: your hosting server and an external service like Dropbox, Google Drive, or Amazon S3.
Retain backups using the 3-2-1 rule: three copies total, on two different media types, with one copy stored off-site. Keep daily backups for 7 days, weekly backups for 4 weeks, and monthly backups for 12 months. This retention strategy lets you recover from problems you don’t discover immediately.
Test your restoration process every 90 days by actually restoring a backup to a staging environment. Download a backup file, follow your recovery documentation step by step, and verify the restored site functions correctly. Many businesses discover their backups are corrupted or incomplete only when they desperately need them.
Step 15: Document your recovery procedures
Write a step-by-step recovery guide that anyone on your team could follow without technical expertise. Document exactly where backups are stored, what credentials are needed to access them, and the precise steps to restore your site. Include contact information for your hosting provider, domain registrar, and any security services you use.
Create a simple recovery checklist in this format:
1. Contact hosting provider immediately: [phone] [email]
2. Access backup storage: [URL] [username]
3. Download most recent clean backup (dated before attack)
4. Delete all infected files via FTP: [credentials]
5. Restore database: [command or process]
6. Upload clean backup files
7. Change all passwords immediately
8. Test site functionality completely
9. Monitor logs for 72 hours post-recovery
Store this documentation outside your website in a secure location like a password manager or encrypted cloud storage. Update the guide immediately after making any changes to your hosting, backup systems, or security tools.
Next steps to keep your site secure
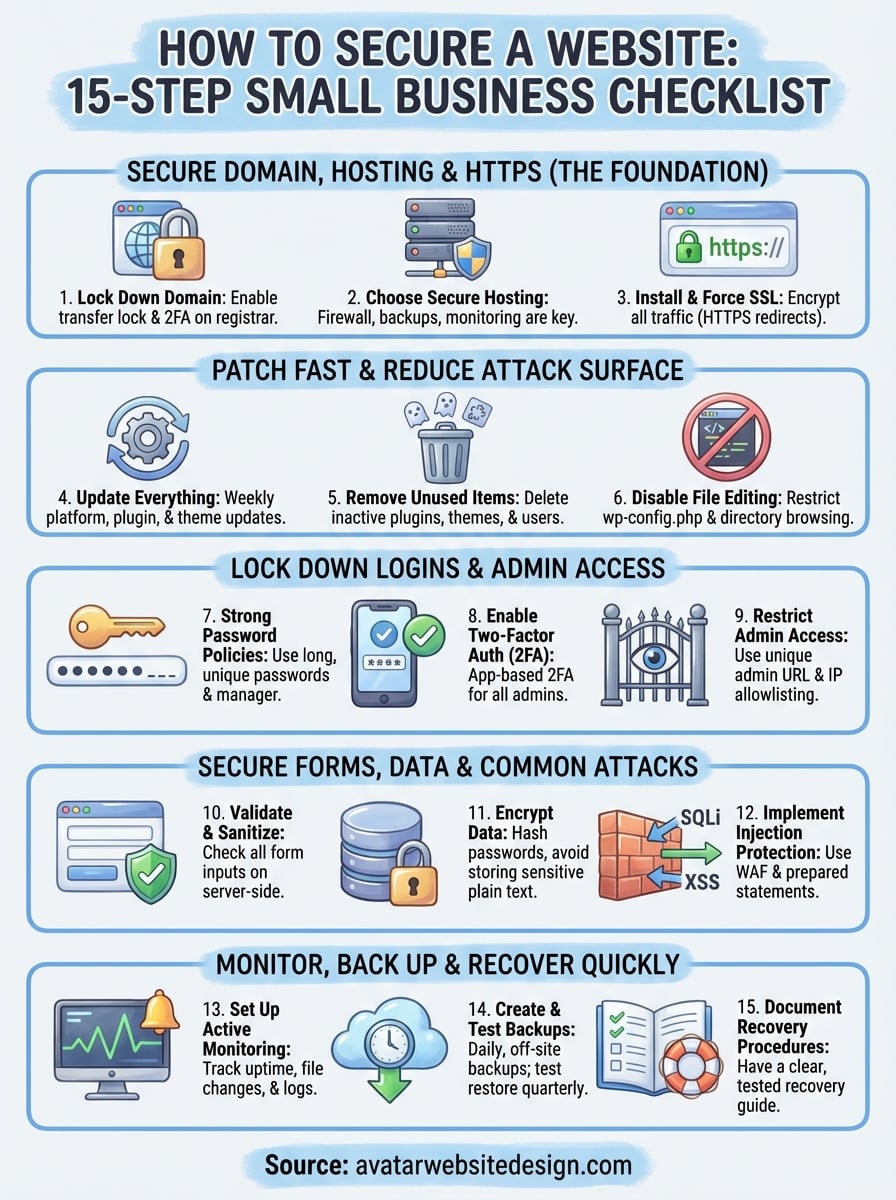
Security isn’t a one-time project. The 15 steps you’ve just completed establish your foundation, but maintaining protection requires ongoing attention. Schedule monthly security reviews to verify your updates are current, your backups are working, and your monitoring hasn’t flagged any threats. Add these reviews to your calendar right now so they don’t slip through the cracks.
Learning how to secure a website means accepting that threats evolve constantly. New vulnerabilities emerge, attackers develop new techniques, and your site changes over time. Stay informed by following security blogs relevant to your platform, but don’t let information overload paralyze you. The steps you’ve implemented today protect against the vast majority of attacks small businesses face.
If managing these security measures feels overwhelming or takes time away from running your business, professional help makes sense. Avatar Website Design handles security maintenance, updates, and monitoring for small business websites, letting you focus on your customers while we protect your online presence.