

Your website is often the first point of contact between your business and potential customers. But it can also be the first target for hackers. Penetration testing for websites, sometimes called pen testing or ethical hacking, is a proactive approach to finding security vulnerabilities before malicious actors do. For small business owners, understanding this process is critical to protecting your online investment.
A pen test simulates real-world attacks on your web application to identify weak points in your security. This includes everything from login forms and payment systems to third-party integrations and server configurations. Knowing what’s at risk allows you to fix problems before they lead to data breaches, financial loss, or damaged customer trust.
At Avatar Website Design, we build websites with security in mind from day one. But security isn’t a one-time effort, it requires ongoing vigilance. That’s why we work closely with our sister company, Avatar Cyber Services, to offer vulnerability assessments and cybersecurity consulting for our clients. In this guide, we’ll walk you through the steps involved in website penetration testing, the tools professionals use, and what you can expect to pay for these essential services.
Why website penetration testing matters
Your website handles sensitive data every day, from customer contact information to payment details. When hackers find a weakness before you do, the consequences can be devastating. Penetration testing for websites helps you discover these vulnerabilities in a controlled environment, allowing you to fix security gaps before they turn into costly breaches.
The real cost of website security breaches
A single security incident can destroy years of hard work building your business. Data breaches cost small businesses an average of $149,000 according to recent industry reports, and that doesn’t account for the long-term damage to your reputation. When customer payment information gets stolen or personal data gets leaked, your business faces legal liability, regulatory fines, and the expensive process of notification and remediation.
Beyond the immediate financial hit, you lose something even more valuable: customer trust. People choose to do business with companies they believe will protect their information. Once that trust breaks, it’s nearly impossible to rebuild. Recovery from a security breach can take months or even years, and some businesses never fully recover.
Regular penetration testing acts as an insurance policy against these catastrophic outcomes, identifying problems while they’re still fixable.
Compliance requirements and industry standards
Many industries require regular security testing as part of their compliance frameworks. If you process credit card payments, PCI DSS compliance mandates annual penetration testing and quarterly vulnerability scans. Healthcare providers handling patient information must meet HIPAA security requirements, which include regular risk assessments and security testing.
Failing to meet these standards results in significant penalties. More importantly, compliance requirements exist because they represent proven security practices. Following them protects your business from known threats and attack patterns that hackers actively exploit.
Proactive security saves money
Fixing security issues before a breach occurs costs a fraction of responding to an actual attack. Proactive testing lets you address vulnerabilities during normal business hours with your existing team or trusted partners. You control the timeline and can implement fixes strategically without the panic and chaos of an emergency response.
Think of penetration testing as routine maintenance for your website’s security. Just as you wouldn’t wait for your car to break down before checking the oil, you shouldn’t wait for a breach to examine your website’s defenses. Regular testing identifies new vulnerabilities introduced through software updates, configuration changes, or emerging attack techniques that didn’t exist when your site first launched.
Pen test vs vulnerability scans and audits
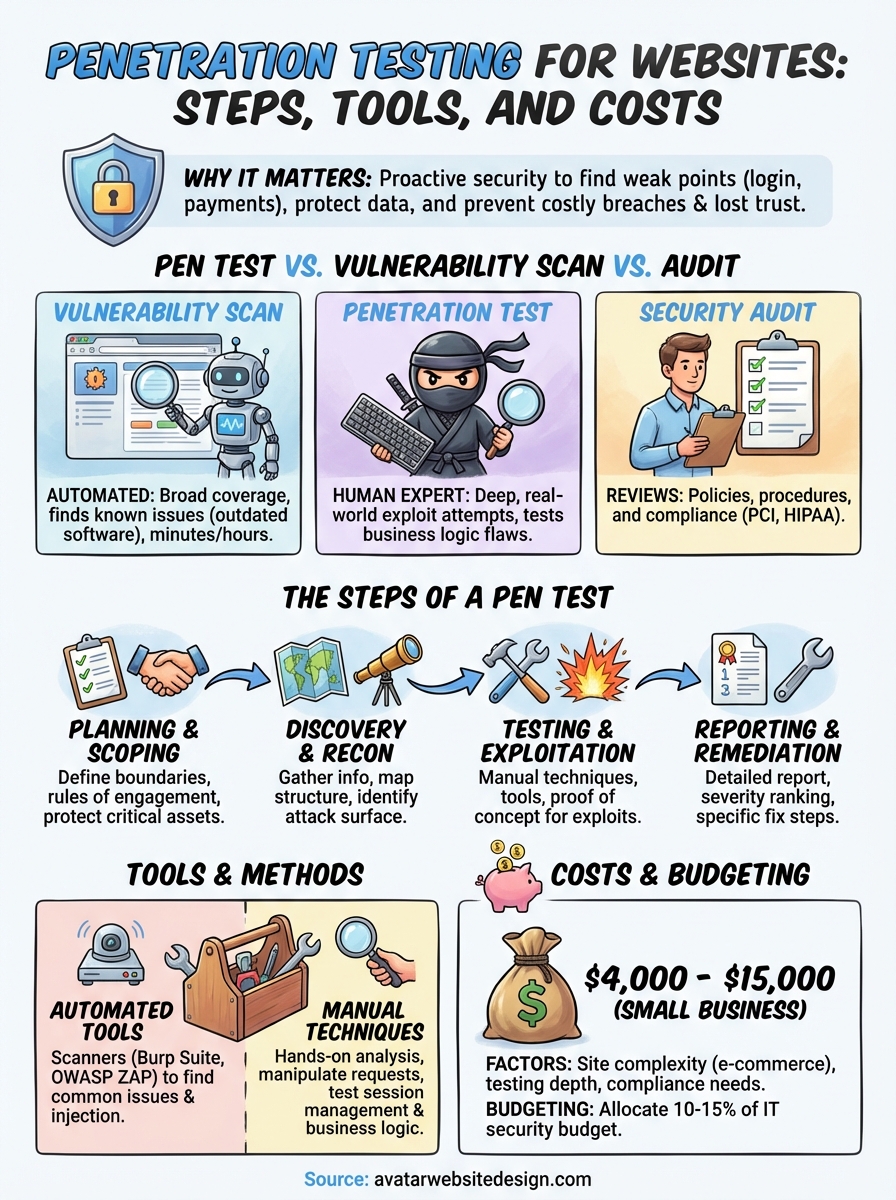
Many small business owners confuse security testing terms, thinking all website security assessments deliver the same results. Understanding the differences between penetration testing for websites, vulnerability scans, and security audits helps you choose the right approach for your specific needs. Each method serves a distinct purpose in your overall security strategy.
What vulnerability scans detect
Vulnerability scanners run automated tools that check your website against databases of known security issues. These scans identify outdated software versions, missing security patches, and common configuration mistakes. The process takes minutes to hours depending on your site’s size, and it produces a report listing potential security weaknesses.
Scanners work well for finding obvious problems like exposed admin panels or default passwords. However, they can’t test whether vulnerabilities are actually exploitable in your specific environment. You might receive dozens of alerts, but many turn out to be false positives that don’t represent real threats to your business.
Automated scans provide breadth of coverage, but they lack the depth and context that human testers bring to security assessments.
Why penetration tests go deeper
Penetration tests involve skilled security professionals who manually attempt to exploit vulnerabilities in your web application. These experts think like attackers, chaining together multiple weaknesses to gain unauthorized access or extract sensitive data. They test business logic flaws that automated scanners miss entirely, such as payment processing errors or authentication bypasses.
A security audit typically reviews your policies, procedures, and security controls against industry standards or compliance requirements. Auditors examine documentation and interview staff but rarely attempt to hack your systems. Penetration tests combine technical expertise with real-world attack scenarios, giving you concrete evidence of what hackers could accomplish. This hands-on approach reveals the actual risk level your business faces from current security gaps.
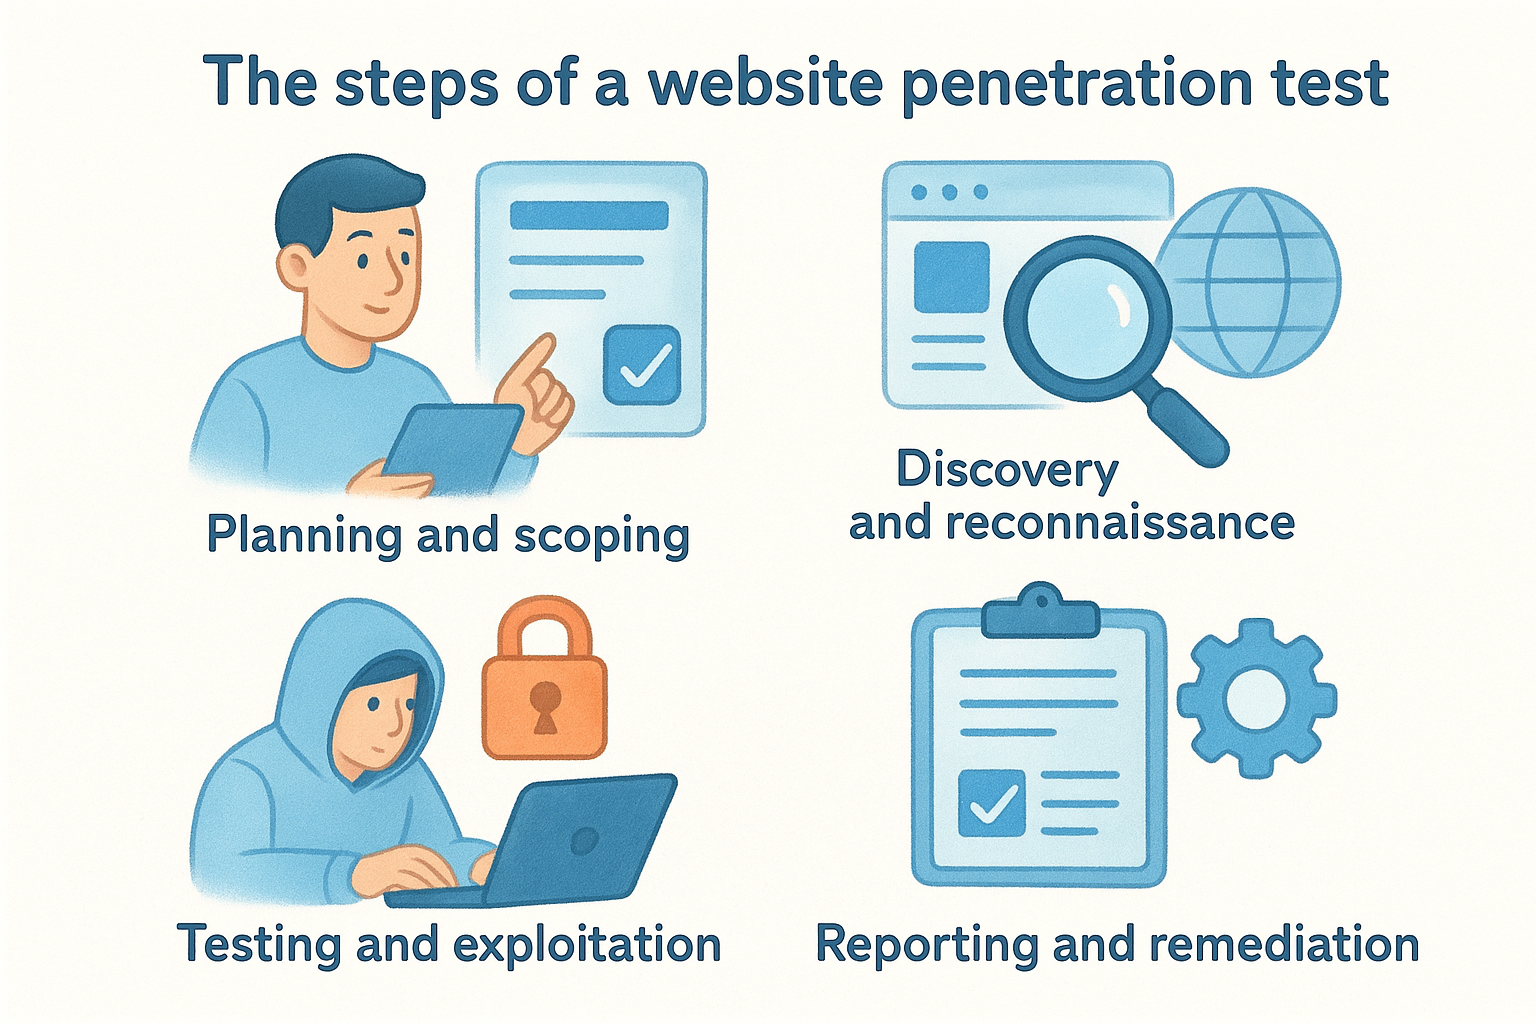
The steps of a website penetration test
Professional penetration testing for websites follows a structured methodology that ensures thorough coverage of your security posture. Each phase builds on the previous one, creating a comprehensive assessment of your web application’s defenses. Understanding these steps helps you know what to expect when you engage security professionals and how the process protects your business.
Planning and scoping the engagement
Your pen test begins with defining exactly what testers can and cannot do. Security professionals work with you to establish clear boundaries around which systems fall within scope, what testing methods are acceptable, and when testing can occur. This planning phase prevents accidental damage to production systems and ensures testers focus on your most critical assets.
You’ll sign agreements that outline the rules of engagement and protect both parties legally. These documents specify whether testers will operate with any insider knowledge or simulate a completely external attacker with no prior information about your systems.
Discovery and reconnaissance
Testers start by gathering information about your website’s infrastructure, technologies, and potential entry points. They map out your application’s structure, identify all input fields, and catalog the software versions your site uses. This reconnaissance phase reveals the attack surface available to potential hackers.
Professional testers document every finding methodically, building a complete picture of your security landscape before attempting any exploits.
Testing and exploitation
Security experts attempt to exploit discovered vulnerabilities using manual techniques and specialized tools. They test authentication systems, injection points, file upload functions, and business logic flaws. Each successful exploit gets documented with proof of concept evidence showing exactly what an attacker could accomplish.
Reporting and remediation
Your pen test concludes with a detailed report ranking vulnerabilities by severity and business impact. Testers provide specific remediation steps for each finding, often including code examples or configuration changes. This documentation becomes your roadmap for improving security and addressing the most critical risks first.
Tools and methods used in website pen testing
Security professionals combine specialized software with manual testing techniques to uncover vulnerabilities that threaten your website. Penetration testing for websites requires both automated tools to identify potential weaknesses and human expertise to determine which findings represent genuine threats. This combination ensures comprehensive coverage while avoiding the false positives that plague purely automated approaches.
Common testing tools professionals rely on
Testers use web application scanners like Burp Suite and OWASP ZAP to intercept traffic between your browser and server. These tools let security experts modify requests, test input validation, and identify injection vulnerabilities that could expose your database. Scanners help map your entire application quickly, discovering hidden pages and administrative interfaces you might not know exist.
Professionals also deploy specialized tools for specific attack types. SQL injection frameworks test database security, password crackers verify authentication strength, and network scanners identify exposed services. Each tool serves a distinct purpose in the testing process, revealing different vulnerability categories.
The most effective penetration tests combine automated scanning with skilled manual verification, catching issues that tools alone would miss entirely.
Manual testing techniques that matter
Experienced testers spend significant time performing hands-on analysis of your application’s behavior. They examine source code in your web pages, test file upload functions with malicious content, and attempt to bypass authentication controls through creative manipulation of requests. This manual work uncovers business logic flaws where your application behaves exactly as programmed but creates security risks.
Security professionals test session management by stealing authentication tokens, verify payment processing logic by manipulating prices, and examine authorization controls by requesting resources they shouldn’t access. These techniques require understanding how your specific business works, not just technical vulnerabilities that automated scanners find.
Costs and how to budget for a pen test
Understanding the financial investment required for website security testing helps you plan appropriately and avoid sticker shock. Penetration testing for websites typically costs between $4,000 and $15,000 for small business web applications, though your specific price depends on several factors. Most security firms charge based on the complexity of your site and the testing depth you need.
Typical cost ranges for small businesses
Basic penetration tests for simple websites with limited functionality start around $4,000 to $6,000. These assessments cover standard security checks, authentication testing, and common vulnerability analysis. More complex sites with e-commerce capabilities, user accounts, or custom features typically cost $8,000 to $12,000 for thorough testing.
Enterprise-level applications or sites requiring compliance documentation can exceed $15,000. Your cost increases when testers need to examine mobile applications, APIs, or multiple integrated systems as part of the same engagement.
Factors that affect pricing
The size of your web application directly impacts testing time and cost. Sites with dozens of pages, multiple user roles, and complex workflows require more hours to test thoroughly than single-page sites. Testing scope also affects pricing if you need specific compliance requirements like PCI DSS validation or detailed remediation support.
Security firms with specialized expertise or industry certifications charge premium rates, but their experience often uncovers issues that less skilled testers miss entirely.
Planning your security budget
You should schedule penetration tests annually at minimum, with quarterly vulnerability scans between full assessments. Budget 10 to 15 percent of your annual IT security spending for testing and remediation work. Setting aside funds specifically for security testing prevents you from cutting corners when urgent updates become necessary after test results arrive.
Conclusion
Penetration testing for websites protects your business from security threats that could destroy everything you’ve built. By identifying vulnerabilities before hackers exploit them, you gain control over your security posture instead of reacting to crises. The investment in professional testing costs far less than recovering from a data breach.
Your website represents your business online, and securing it requires expertise you might not have in-house. Regular testing combined with proactive remediation keeps your customer data safe and your business compliant with industry standards. Professional guidance makes the difference between a secure website and one waiting to become tomorrow’s headline.
At Avatar Website Design, we build websites with security as a foundation, not an afterthought. Our partnership with Avatar Cyber Services ensures your site stays protected through comprehensive security assessments and ongoing monitoring. Let us help you protect your online investment and maintain the trust your customers place in your business.