

Squarespace handles a lot of security out of the box, SSL certificates, infrastructure monitoring, DDoS protection. For most small business owners, that’s a major reason they chose the platform in the first place. But "managed" doesn’t mean "maintenance-free," and Squarespace website security still requires you to configure the right settings and understand what’s actually protecting your site.
We see this regularly at Avatar Website Design. A client launches on Squarespace assuming everything is locked down, then runs into a "Not Secure" browser warning or realizes they never turned on two-factor authentication. These aren’t rare edge cases, they’re common gaps that put your business and your visitors at risk. The good news: most fixes take minutes, not hours.
This article breaks down how Squarespace security works, what’s built in, what you need to enable yourself, and how to troubleshoot the most frequent security warnings. Whether you’re setting up a new Squarespace site or tightening up an existing one, you’ll walk away with clear, specific steps to keep your site and your customer data protected.
What Squarespace website security covers
Squarespace website security operates on a shared responsibility model. Squarespace controls the infrastructure layer, meaning the servers, the network, and the core platform stay protected without you touching a single setting. But you still own the top layer: your account credentials, your site configuration, and every decision you make about who gets access to what. Understanding that boundary is the first step to running a genuinely secure site.
Built-in protections Squarespace manages for you
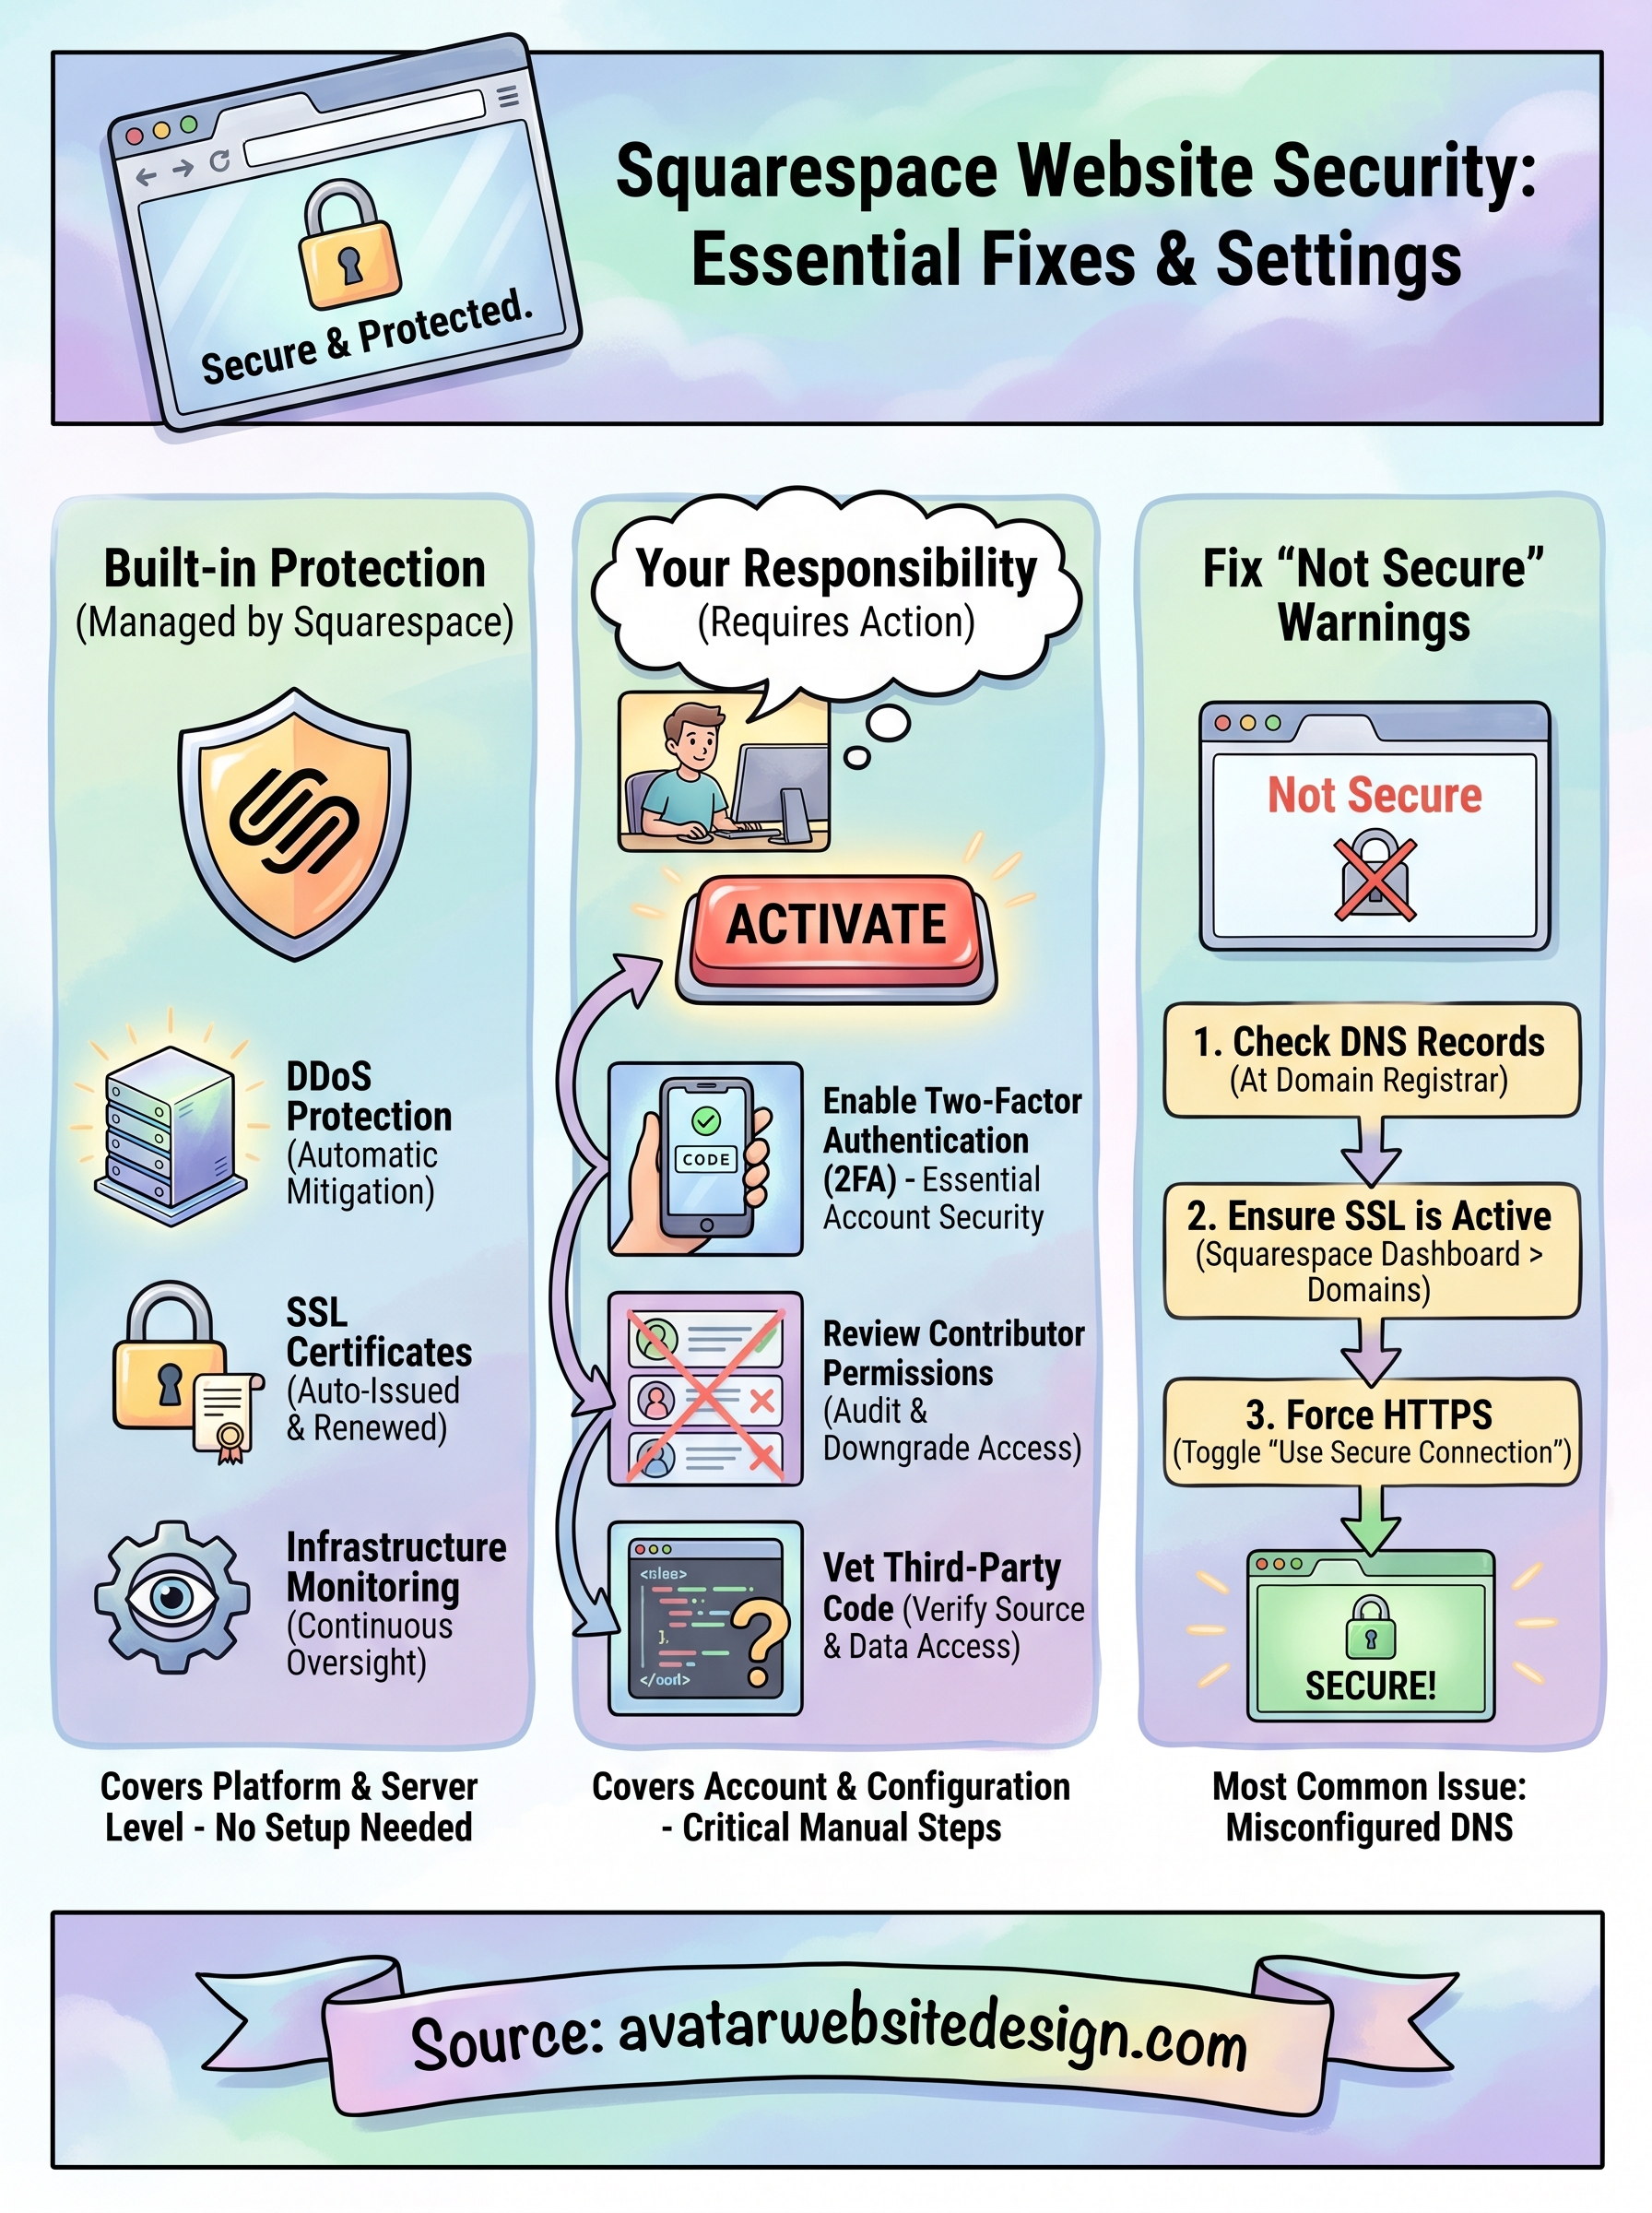
Squarespace handles several security layers automatically as part of every hosted plan. The platform sits behind DDoS protection, which absorbs large-scale traffic attacks before they ever reach your site. It also runs continuous infrastructure monitoring to flag unusual activity at the server level. None of this requires configuration on your end; it runs the moment your site goes live and stays active throughout your subscription.
These built-in protections are substantial, but they only cover the platform itself, not the choices you make inside your account or the third-party code you add to your pages.
Beyond attack mitigation, Squarespace issues and renews SSL certificates automatically for every site on the platform. It also pushes software updates and security patches without any action from you, which removes one of the biggest risks that comes with self-hosted platforms like WordPress, where outdated plugins and core files are a constant vulnerability. Here’s a breakdown of what Squarespace handles on your behalf:
- DDoS mitigation at the network level
- SSL/TLS certificates, issued and renewed at no extra cost
- Server-side software updates and security patches
- Physical data center security and access controls
- Platform-level uptime monitoring
What you’re still responsible for
The built-in protections stop at the platform boundary. Everything above that, your login credentials, contributor account permissions, domain settings, and any external code you add to your site, falls on you to manage correctly. A weak administrator password or an old contributor account you forgot to remove can expose your entire site regardless of how strong Squarespace’s infrastructure happens to be.
Third-party scripts and integrations introduce a category of risk that Squarespace simply cannot cover. When you embed a custom code block or connect a third-party tool through an API, that code runs directly on your site with access to your visitors’ sessions and data. Squarespace monitors its own platform, but it does not audit external scripts you inject manually through the code editor or header injection settings. Before adding any third-party code to your site, verify the source, check that it comes from a reputable provider, and review what data it accesses.
Why SSL matters and how Squarespace handles it
SSL (Secure Sockets Layer) is the technology that encrypts data traveling between your visitor’s browser and your web server. When SSL is active, that connection displays a padlock icon in the browser address bar and uses "https" instead of "http." Without it, browsers like Chrome flag your site as "Not Secure," which pushes visitors away before they read a single word of your content.
What SSL actually does for your visitors
SSL protects sensitive information your visitors submit through your site, including contact form entries, email addresses, and payment details. Without an active SSL certificate, that data travels in plain text, which means anyone intercepting the connection can read it. This is a real liability that affects both visitor trust and your search rankings, since Google factors HTTPS into how it scores pages.
Google has confirmed that HTTPS is a ranking signal, meaning a missing SSL certificate can directly suppress your site’s visibility in search results.
How Squarespace provisions SSL
Squarespace automatically issues and renews SSL certificates for every site on its platform at no additional charge. When you connect a custom domain to your Squarespace site, the platform detects it and provisions the certificate within 72 hours. You do not need to purchase a certificate separately, manage renewal dates, or configure server settings manually.
The most common situation where SSL fails on a Squarespace site involves a misconfigured domain. If your DNS records don’t point correctly to Squarespace’s servers, the platform cannot issue or validate the certificate for your domain. This accounts for most "Not Secure" warnings that appear even when squarespace website security settings look correct on the surface. Checking your domain’s DNS configuration in your registrar’s control panel is always the right first step when SSL fails to activate.
How to secure your Squarespace site settings
Your site-level settings inside Squarespace are the most overlooked layer of squarespace website security. The platform protects the infrastructure, but your configuration choices inside the dashboard determine whether that protection actually extends to your visitors. Two areas deserve your attention before anything else: contributor permissions and your domain’s SSL status.
Control who can access your site
Squarespace lets you add contributors at different permission levels, from full administrators down to billing-only access. Every contributor account you create is a potential entry point, and old or unnecessary accounts are one of the most common ways sites get compromised. Go to the Permissions panel in your Squarespace dashboard and audit every account listed there.
Remove any contributor who no longer actively works on your site, and downgrade any account that does not need administrator-level access.
When you do need to grant access, match the permission level to the task. A copywriter does not need admin rights. A billing contact does not need the ability to edit pages. Squarespace gives you granular control here, and using it correctly limits the damage any single compromised account can cause.
Review your domain and SSL settings
Inside your Squarespace dashboard, navigate to Domains and confirm that your custom domain shows an active SSL certificate. Squarespace displays this status clearly, and it should read as secure for every connected domain. If it does not, the issue almost always traces back to DNS misconfiguration at your domain registrar, not a problem inside Squarespace itself.
Check that your domain’s CNAME or A records point exactly to the values Squarespace requires. Your registrar’s DNS management panel is where you make those corrections. Once the records propagate correctly, Squarespace provisions the certificate automatically, typically within 24 to 72 hours. No manual certificate installation is needed on your end.
How to lock down your Squarespace account
Your Squarespace account is the single access point that controls everything on your site. A compromised account gives an attacker full administrative control, including the ability to delete pages, inject malicious code, or lock you out entirely. Two settings directly address this risk: two-factor authentication (2FA) and a strong, unique password. Both take less than five minutes to set up, and both are essential for solid squarespace website security.
Enable two-factor authentication
Two-factor authentication adds a second verification step every time someone tries to log into your account. Even if someone steals your password, they cannot get in without the second factor, which is typically a code generated by an authenticator app on your phone. Squarespace supports 2FA natively and recommends enabling it for every account that has administrative access.
Enabling 2FA is the single most effective step you can take to prevent unauthorized access to your Squarespace account.
To turn it on, go to your account settings, select "Security," and follow the prompts to connect an authenticator app. Google Authenticator and similar apps work with Squarespace’s 2FA setup. Once active, every login requires your password plus a time-sensitive code from the app, which resets every 30 seconds and cannot be reused.
Use a strong, unique password
Your account password is the first barrier between your site and anyone trying to access it without your permission. Using a password you reuse across other accounts creates serious exposure, because a breach on any other platform can hand attackers working credentials for your Squarespace login. Choose a password that is at least 16 characters and does not appear anywhere else you log in.
A password manager is the practical solution here. It generates complex, unique passwords for every account and stores them securely, so you do not have to memorize them or write them down anywhere that creates additional risk.
How to fix a Squarespace site that says not secure
A "Not Secure" warning in your browser means one thing: SSL is not active on your domain. This is one of the most common squarespace website security issues small business owners run into, and it almost always has a straightforward cause. Before you assume something is broken inside Squarespace, understand that the platform itself rarely causes this warning. The problem almost always originates outside Squarespace, in your domain’s DNS settings.
Check your DNS records first
Your domain registrar controls how your domain points to Squarespace’s servers, and incorrect DNS records are the leading cause of SSL failures on Squarespace sites. When those records are wrong, Squarespace cannot validate ownership of your domain and will not issue the certificate. Log into your domain registrar’s control panel and compare your current DNS records against the exact values Squarespace provides in your Domains settings.
Squarespace publishes the required DNS values directly in your dashboard under Domains, so you always have the correct target records available without contacting support.
Look specifically at your CNAME record for "www" and your A records for the root domain. Both need to point to Squarespace’s specified addresses. Once you correct the records, propagation typically completes within 24 to 72 hours, after which Squarespace automatically provisions your SSL certificate without any further action from you.
Force HTTPS after SSL activates
Once SSL is active, you need to confirm that Squarespace redirects all traffic to the secure HTTPS version of your site. Inside your Squarespace dashboard, navigate to Domains, select your custom domain, and look for the "Use Secure Connection" toggle. Make sure it is turned on. This setting forces every visitor to the encrypted version of your site and eliminates any mixed-content warnings that appear when some page elements still load over HTTP.
Quick wrap-up and next steps
Squarespace website security gives you a strong foundation, but the platform can only do so much on its own. You need SSL active on your custom domain, two-factor authentication enabled on your account, contributor permissions trimmed to only what each person actually needs, and HTTPS forced across every page. These settings protect both your business and every visitor who lands on your site.
If you ran through this guide and realized your site needs more than a few setting tweaks, that is a signal worth paying attention to. A professionally built site starts with security and structure built in from day one, not retrofitted after the fact. At Avatar Website Design, we build websites for small businesses that are mobile-ready, SEO-optimized, and configured correctly from the start. If you are ready to get your business online the right way, reach out to our web design team and we will walk you through it.