

Small businesses are prime targets for cyberattacks, not because they have the most valuable data, but because they often have the weakest defenses. Following website security best practices isn’t optional anymore; it’s essential for protecting your customers, your reputation, and your bottom line.
The consequences of a security breach go far beyond a temporary headache. Compromised customer data can lead to legal liability, lost trust, and permanent damage to your brand. For many small businesses, a single attack can cost thousands in recovery, or worse, force them to close their doors entirely.
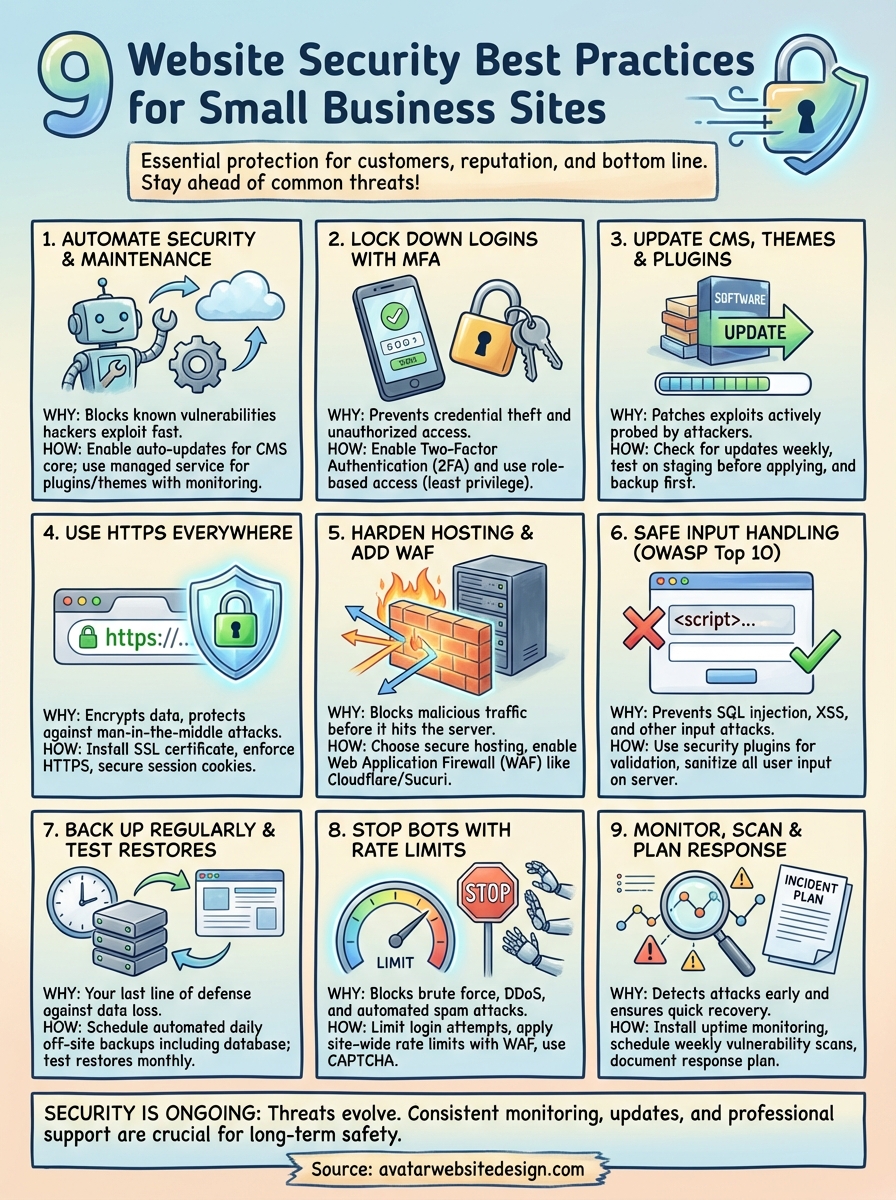
At Avatar Website Design, we build and maintain websites for small businesses every day, and security is baked into everything we do. This guide breaks down nine actionable steps you can take to protect your site, covering everything from SSL certificates and access controls to regular backups and vulnerability scanning. Whether you manage your own website or work with a professional team, these practices will help you stay ahead of common threats and keep your business running safely online.
1. Put security and maintenance on autopilot
Manual security updates are the most common way small business sites get compromised. You can follow every other security guideline perfectly, but if you skip a single critical patch, attackers will find that vulnerability within hours. Automating your security updates and maintenance removes human error from the equation and ensures your site stays protected around the clock.
What it protects you from
Automated maintenance shields your site from known vulnerabilities that hackers actively scan for and exploit. When software developers discover security flaws in WordPress, plugins, or themes, they release patches immediately. Attackers know these vulnerabilities exist and target sites that haven’t updated yet, often within 24 hours of a public disclosure. Automation closes that window before criminals can act.
The average website gets attacked 44 times per day, and outdated software accounts for the majority of successful breaches.
How to implement it on a small business site
Start by enabling automatic updates for your CMS core files through your hosting control panel or WordPress settings. Most reputable hosting providers offer automatic updates as a standard feature. For plugins and themes, choose a managed maintenance service that monitors, tests, and applies updates for you rather than relying on built-in auto-update features that can break your site without warning.
Professional maintenance plans typically include daily backups, security scanning, uptime monitoring, and expert support when something goes wrong. These services cost between $50 and $200 per month depending on your site’s complexity, but they prevent the thousands of dollars in recovery costs that follow a breach.
Common mistakes to avoid
The biggest mistake is assuming automatic updates work without supervision. Updates can occasionally conflict with custom code or cause compatibility issues between plugins. Without testing and monitoring, you might not notice a broken feature until customers complain. Always pair automation with regular functionality checks and keep a recent backup before major updates.
Another critical error is automating everything without reviewing what gets updated. Some plugins or themes might have been abandoned by their developers, and automatic updates won’t happen if the software isn’t actively maintained. Check your installed plugins quarterly and replace any that haven’t been updated in six months, as these represent serious security risks.
2. Lock down logins with MFA and least privilege
Weak login security remains the easiest way for attackers to take over your website. Multi-factor authentication (MFA) and role-based access controls turn your login page from an open door into a fortress that stops unauthorized access before it starts.
What it protects you from
MFA blocks credential theft attacks even when hackers steal your password through phishing emails or data breaches. Attackers need both your password and a second verification method (like a code from your phone), which they can’t easily obtain. Role-based access ensures that compromised accounts can only access the features they need, limiting damage if someone breaks in.
How to implement it on a small business site
Enable two-factor authentication on every admin account immediately through your hosting control panel or a security plugin. WordPress users can install free plugins like Google Authenticator that add MFA in minutes. Create separate accounts for each team member and assign the minimum permissions they need, following the principle of least privilege. A content writer doesn’t need plugin installation rights, and your web developer shouldn’t have access to your payment gateway.
99.9% of automated attacks fail when multi-factor authentication is enabled, according to Microsoft security research.
Common mistakes to avoid
Never share admin credentials between multiple people or rely on SMS-based verification codes as your only second factor. SMS messages can be intercepted through SIM swapping attacks. Use authenticator apps or hardware security keys instead for true protection that aligns with website security best practices.
3. Keep your CMS, themes, and plugins updated
Outdated software creates the biggest security holes in small business websites. Every piece of code running your site, from WordPress core to individual plugins, needs regular updates to patch vulnerabilities that hackers actively exploit. Keeping everything current isn’t just good housekeeping, it’s one of the most essential website security best practices you can implement.
What it protects you from
Software updates protect you from known exploits that criminals scan for automatically. Hackers use automated tools that probe thousands of sites per hour looking for outdated WordPress versions, vulnerable plugins, or unpatched themes. When developers discover security flaws, they release fixes immediately, but your site remains at risk until you apply those patches.
Outdated plugins and themes account for 29% of all WordPress hacks, making them the second most common entry point for attackers.
How to implement it on a small business site
Check for updates weekly through your WordPress dashboard under Updates. Before updating anything, create a fresh backup so you can restore quickly if something breaks. Update your CMS core files first, then themes, and finally plugins in that specific order to minimize compatibility issues. Test critical functions like contact forms, checkout pages, and login systems after each round of updates.
Common mistakes to avoid
Running updates on a live site without testing them first creates unnecessary risks. Use a staging environment to test updates before pushing them to production, or at minimum, schedule updates during off-peak hours when traffic is lowest. Another dangerous habit is ignoring update notifications because you’re busy. Those alerts signal active security threats that worsen with each passing day.
4. Use HTTPS everywhere and secure your sessions
Unencrypted connections expose your customers’ data and login credentials to anyone monitoring the network. HTTPS encryption transforms your website from a public postcard into a sealed envelope, protecting every interaction between visitors and your server. Session security goes beyond encryption by ensuring that authenticated users stay protected throughout their entire visit to your site.
What it protects you from
HTTPS stops man-in-the-middle attacks where hackers intercept data traveling between your server and visitors’ browsers. Without encryption, attackers on public WiFi networks can capture passwords, payment information, and personal details in plain text. Secure session management prevents session hijacking, where criminals steal active login tokens to impersonate legitimate users and access restricted areas of your site.
Sites without HTTPS lose 85% of potential customers who see browser warnings about insecure connections, according to Google transparency reports.
How to implement it on a small business site
Install an SSL/TLS certificate through your hosting provider, which typically offers free certificates through Let’s Encrypt. Enable HTTPS in your WordPress settings and redirect all HTTP traffic to HTTPS automatically using your .htaccess file or a security plugin. Configure secure session cookies by enabling the httpOnly and secure flags in your CMS settings, which prevents JavaScript from accessing session tokens and ensures they only transmit over encrypted connections.
Common mistakes to avoid
Mixed content warnings occur when your site loads images or scripts over HTTP while the main page uses HTTPS, breaking the security indicator in browsers. Scan your entire site after enabling HTTPS to fix hardcoded HTTP links. Another critical error is setting session timeout periods too long, which gives attackers more time to exploit stolen credentials. Limit active sessions to 30 minutes for admin accounts and require re-authentication for sensitive actions like payment processing or profile changes.
5. Harden hosting and add a web firewall
Your hosting environment forms the foundation of your site’s security, and a weak foundation guarantees eventual compromise. Server hardening and web application firewalls (WAF) create layers of defense that stop attacks before they reach your website code, making them critical components of comprehensive website security best practices.
What it protects you from
A WAF blocks malicious traffic patterns and known attack signatures before they hit your server. These firewalls filter out SQL injection attempts, cross-site scripting attacks, and automated vulnerability scans that probe for weaknesses. Hardened hosting prevents server-level exploits by disabling unnecessary services, restricting file permissions, and limiting access to sensitive directories that attackers target during reconnaissance.
Websites with web application firewalls experience 90% fewer successful attacks compared to unprotected sites, according to Cloudflare security data.
How to implement it on a small business site
Choose a hosting provider that includes built-in security features like automated malware scanning, DDoS protection, and isolated hosting environments. Enable your host’s WAF through the control panel or add a third-party service like Cloudflare or Sucuri that sits between visitors and your server. Request that your hosting provider disable unused server functions, change default SSH ports, and implement fail2ban to automatically block repeated failed login attempts.
Common mistakes to avoid
Relying solely on a WAF without hardening your server leaves backdoor vulnerabilities that sophisticated attackers will find. Configure your firewall rules to match your actual traffic patterns rather than using default settings that might block legitimate users. Another error is choosing budget hosting that crams hundreds of sites onto shared servers, where one compromised neighbor can provide attackers access to your files through improper isolation.
6. Block OWASP Top 10 issues with safe input handling
Input validation failures create the most dangerous vulnerabilities on small business websites. Every form field, URL parameter, and user submission represents a potential attack vector that criminals exploit to inject malicious code or extract sensitive data. Proper input handling blocks these attempts before they reach your database or execute on your server, making it one of the most critical website security best practices you can implement.
What it protects you from
Safe input handling prevents SQL injection attacks where hackers manipulate database queries to steal customer records, delete data, or take over admin accounts. It also stops cross-site scripting (XSS) where attackers inject JavaScript that steals session cookies or redirects visitors to phishing sites. These vulnerabilities make up six of the OWASP Top 10 security risks that target web applications, representing the most common and dangerous threats your site faces.
The OWASP Top 10 accounts for 94% of successful web application attacks, making input validation your most important defensive measure.
How to implement it on a small business site
Install a security plugin that includes input validation features and automatically sanitizes form submissions. WordPress users can deploy plugins like Wordfence or iThemes Security that filter malicious input patterns. Configure your CMS to escape all output, validate data types for each form field, and reject suspicious characters in user inputs. Use parameterized queries for database operations instead of concatenating user input directly into SQL statements.
Common mistakes to avoid
Validating input only on the client side using JavaScript gives you zero protection because attackers bypass browser validation easily. Always validate and sanitize data on your server where criminals can’t circumvent your checks. Another dangerous practice is whitelisting specific characters instead of blacklisting dangerous ones, since attackers constantly discover new exploitation techniques that slip past blacklists.
7. Back up your site and test restores regularly
Backups serve as your last line of defense when every other security measure fails. A verified backup strategy turns catastrophic data loss into a minor inconvenience, letting you restore your site completely after ransomware attacks, server failures, or accidental deletions. Testing those backups regularly ensures they actually work when you need them most, making this one of the most overlooked yet essential website security best practices.
What it protects you from
Regular backups protect you from permanent data loss caused by successful attacks, hardware failures, or human error. Ransomware attackers encrypt your files and demand payment for the decryption key, but a clean backup lets you ignore their threats and restore immediately. Backups also safeguard against insider threats, corrupted databases, and hosting provider failures that can erase months or years of work in seconds.
Companies without tested backup procedures take an average of 23 days to recover from a ransomware attack, compared to just 2 days for those with working backups.
How to implement it on a small business site
Schedule automated daily backups through your hosting provider or a dedicated backup service that stores copies off-site. Configure your backup solution to include your database, uploaded files, themes, and plugins in every snapshot. Test restores monthly by actually recovering your site to a staging environment to verify that your backups work correctly and contain all necessary files.
Common mistakes to avoid
Storing backups only on the same server as your website creates single point of failure that attackers exploit by deleting backups before encrypting your files. Keep at least three copies in different physical locations, including cloud storage with versioning enabled. Another critical error is assuming backups work without testing them, which leaves you discovering corrupted or incomplete backups only after disaster strikes.
8. Stop bots, brute force, and DDoS with rate limits
Automated attacks overwhelm small business websites through sheer volume, attempting thousands of login combinations per second or flooding your server with traffic until it crashes. Rate limiting controls how many requests your site accepts from a single source within a specific timeframe, stopping these attacks before they consume your resources or crack your accounts.
What it protects you from
Rate limiting blocks brute force attacks where bots systematically try every possible password combination to break into admin accounts. It also prevents distributed denial of service (DDoS) attacks that send massive amounts of traffic to make your site unavailable to real customers. Malicious bots that scrape your content, test for vulnerabilities, or submit spam through contact forms get shut down automatically when they exceed normal usage patterns.
Brute force attacks succeed against 65% of websites without rate limiting protection, typically within 72 hours of targeting a site.
How to implement it on a small business site
Enable login attempt limits through your security plugin, typically restricting each IP address to five failed attempts before implementing a temporary lockout. Configure your WAF to apply rate limits on your entire site, blocking IPs that exceed 60 requests per minute. Add CAPTCHA challenges to forms after detecting suspicious activity patterns, which stops automated submissions while allowing legitimate users through.
Common mistakes to avoid
Setting rate limits too aggressively blocks legitimate users who share IP addresses on corporate networks or mobile carriers. Monitor your traffic patterns for a week before implementing strict limits. Another error is rate limiting only your login page while leaving API endpoints and form submissions unprotected, which gives attackers alternative entry points to exploit your site.
9. Monitor, scan, and plan your incident response
Security monitoring and incident response planning transform reactive firefighting into proactive threat management. Continuous monitoring detects attacks as they happen, vulnerability scanning finds weaknesses before criminals do, and a documented response plan ensures your team knows exactly what to do when (not if) a security incident occurs. These three components complete your website security best practices by preparing you for threats that slip past your other defenses.
What it protects you from
Active monitoring catches ongoing attacks and unusual behavior patterns that indicate compromised accounts, malware infections, or data breaches in progress. Vulnerability scanners identify configuration errors and outdated components that create security holes in your site. An incident response plan prevents panic decisions during crises and reduces downtime by establishing clear procedures for containment, recovery, and communication when attacks succeed.
Organizations with documented incident response plans reduce breach costs by $2.66 million on average compared to those without plans.
How to implement it on a small business site
Install uptime monitoring that alerts you immediately when your site goes offline or loads slowly. Schedule weekly vulnerability scans through your security plugin or hosting provider to detect new threats and misconfigurations. Document a simple incident response plan that includes emergency contacts, backup restoration steps, and procedures for notifying customers if their data gets compromised.
Common mistakes to avoid
Collecting monitoring alerts without reviewing them regularly turns your security tools into noise generators that you’ll ignore during actual incidents. Check your security logs weekly and investigate suspicious patterns immediately. Another critical error is creating incident response plans that sit unused in a drawer, which leaves your team unprepared when real attacks demand quick action and clear decisions.
Next steps
Implementing these nine website security best practices protects your business from the attacks that compromise thousands of small business sites every month. You don’t need to be a security expert to keep your site safe, but you do need consistent attention and professional support to maintain your defenses over time.
Security isn’t a one-time project you complete and forget. Threats evolve constantly, requiring ongoing monitoring, updates, and adjustments to your protection strategy. Many small business owners find that managing security themselves takes time away from running their actual business.
Avatar Website Design builds websites with security baked into every layer and offers comprehensive maintenance plans that handle updates, backups, monitoring, and threat response for you. Our team stays current on emerging threats and implements protections before attackers can exploit new vulnerabilities, letting you focus on growing your business while we keep your digital presence secure.