

When you visit a website and see that little padlock icon in your browser’s address bar, you’re looking at an SSL certificate in action. But what is an SSL certificate exactly, and why does every small business website need one?
At Avatar Website Design, we build websites for small businesses every day, and one of the first things we ensure is proper SSL implementation. Without it, your site gets flagged as "Not Secure" by browsers, which sends potential customers running before they even see what you offer. Beyond the trust factor, SSL certificates directly impact your search engine rankings and protect sensitive customer data from interception.
This guide breaks down everything you need to know: how the encryption process actually works, why Google treats SSL as a ranking signal, and which certificate type makes sense for your business. Whether you’re launching your first website or trying to figure out why your current site shows security warnings, you’ll walk away with clear answers and a solid understanding of how to keep your website, and your visitors, protected.
What an SSL certificate is
An SSL certificate is a small data file that lives on your web server and creates an encrypted connection between your website and your visitor’s browser. Think of it as a digital passport that verifies your website’s identity and enables secure data transmission. When someone enters information on your site (credit card numbers, passwords, contact details), the SSL certificate scrambles that data into unreadable code during transit, making it nearly impossible for hackers to intercept and steal.
The digital certificate explained
Your SSL certificate contains specific information about your website and business. It holds your domain name, your company name (for certain certificate types), and the certificate’s expiration date. The certificate also includes a pair of cryptographic keys: a public key that encrypts data and a private key that decrypts it. When someone visits your site, their browser checks this certificate to confirm you are who you claim to be before establishing that secure connection.
The certificate gets issued by a Certificate Authority (CA), which acts as a trusted third party that verifies your identity before handing over the certificate. Organizations like DigiCert, Let’s Encrypt, and Sectigo function as CAs. They perform various levels of validation (depending on which certificate type you purchase) to ensure you legitimately control the domain and, in some cases, that your business legally exists.
An SSL certificate transforms your site from "http://" to "https://" and displays that padlock icon that tells visitors their connection is secure.
What SSL actually stands for (and what it’s called now)
SSL stands for Secure Sockets Layer, which was the original encryption protocol developed in the mid-1990s. However, SSL has been officially deprecated for years. The technology you’re actually using today is called TLS (Transport Layer Security), which replaced SSL back in 1999. Despite this technical accuracy, most people still say "SSL certificate" because the term stuck around. When you see "SSL/TLS certificate" or just "SSL," both refer to the same modern encryption technology that protects websites today.
Understanding what is an SSL certificate matters because you’ll encounter these terms when setting up your website, purchasing hosting, or troubleshooting security warnings. The underlying technology has evolved significantly since those early SSL days, but the core purpose remains the same: creating secure, encrypted connections that protect your visitors and build trust in your online presence. Your hosting provider might list certificates as "SSL," "TLS," or "SSL/TLS" interchangeably, and they all accomplish the same security goals for your website.
Why SSL certificates matter for small businesses
Your customers judge your website in seconds, and browser warnings about "Not Secure" connections destroy that first impression before visitors even read your content. Beyond appearances, SSL certificates directly impact three critical areas of your online business: search engine visibility, customer trust, and payment processing compliance. Understanding what is an ssl certificate and implementing one isn’t optional anymore; it’s a fundamental requirement for running a legitimate online presence.
Google ranks secure sites higher
Google officially confirmed in 2014 that HTTPS serves as a ranking signal, and they’ve steadily increased its importance since then. Websites without SSL certificates receive a ranking penalty compared to identical sites with proper encryption. Chrome, Firefox, and Safari all display prominent "Not Secure" warnings on pages without SSL, which increases your bounce rate and signals poor user experience to search engines. This creates a compounding effect where lack of SSL hurts both your direct rankings and your behavioral metrics that Google uses to evaluate site quality.
Browser warnings kill conversions instantly
When potential customers see security warnings on your site, 70% of them leave immediately according to browser behavior studies. That padlock icon in the address bar acts as a visual trust signal that tells visitors their information stays protected. Without it, you’re asking people to share contact details, make purchases, or submit forms on a site their browser actively warns them about. The conversion damage extends beyond checkout pages, affecting every form submission, newsletter signup, and contact inquiry across your entire website.
Modern browsers flag ALL non-HTTPS pages as insecure, not just checkout pages, meaning every visitor sees warnings regardless of whether they’re entering sensitive data.
Compliance requirements demand SSL protection
Payment processors like Stripe and PayPal mandate SSL certificates as part of PCI DSS compliance before they’ll process transactions through your site. Without proper encryption, you violate these security standards and risk losing payment processing capabilities entirely. Insurance companies, healthcare providers, and financial services face even stricter data protection regulations that make SSL certificates a legal requirement rather than a technical nicety.
How SSL certificates work in plain English
Understanding what is an ssl certificate becomes clearer when you see the actual process in action. When someone visits your website, a complex exchange happens in milliseconds that you never see. Your visitor’s browser and your web server perform a series of verification steps and establish an encrypted tunnel through which all data travels. This entire process happens automatically every time someone loads a page on your site, creating a secure connection that protects information from prying eyes.
The handshake process that happens instantly
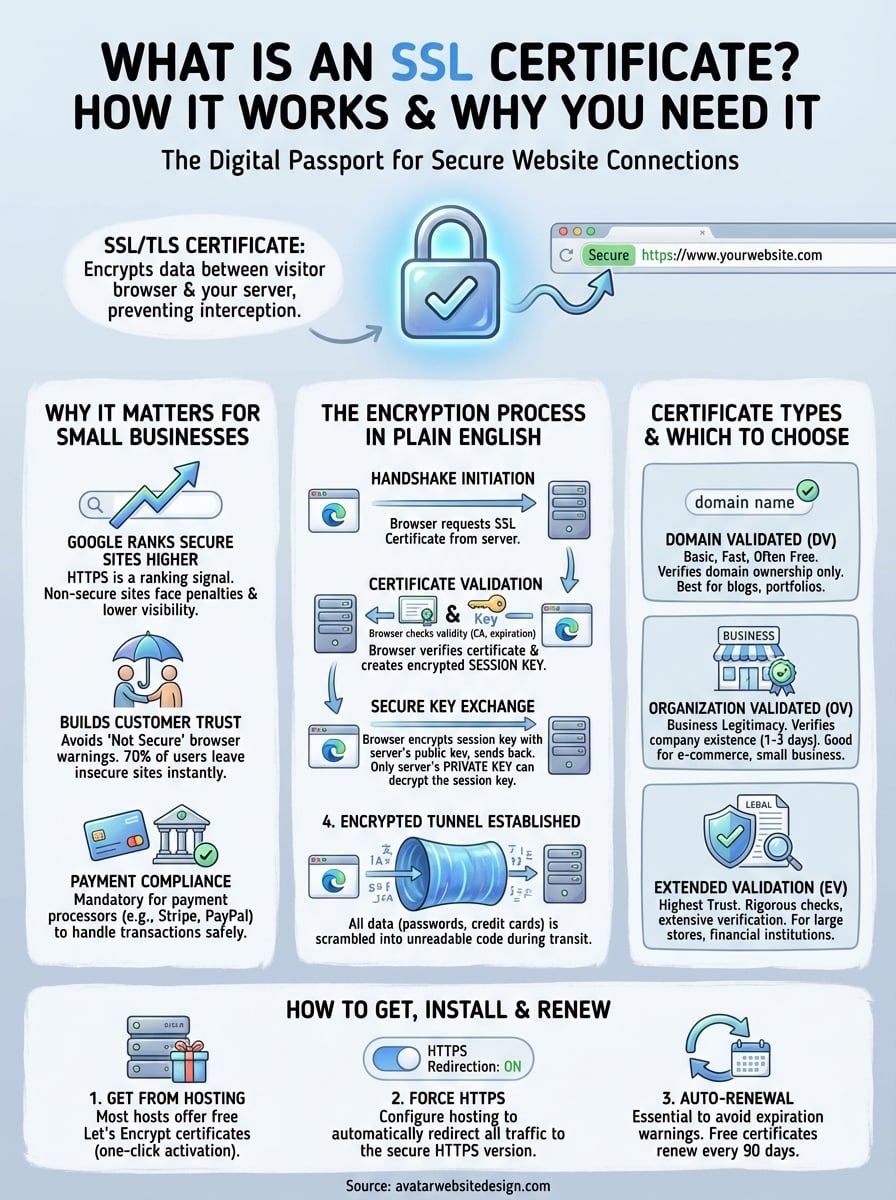
The moment a visitor types your website address, their browser reaches out to your server and requests the SSL certificate. Your server sends back the certificate along with its public key, and the browser immediately checks whether the certificate is valid, properly signed by a trusted Certificate Authority, and hasn’t expired. If everything checks out, the browser generates a session key (a temporary encryption key used just for this visit) and encrypts it using your server’s public key before sending it back.
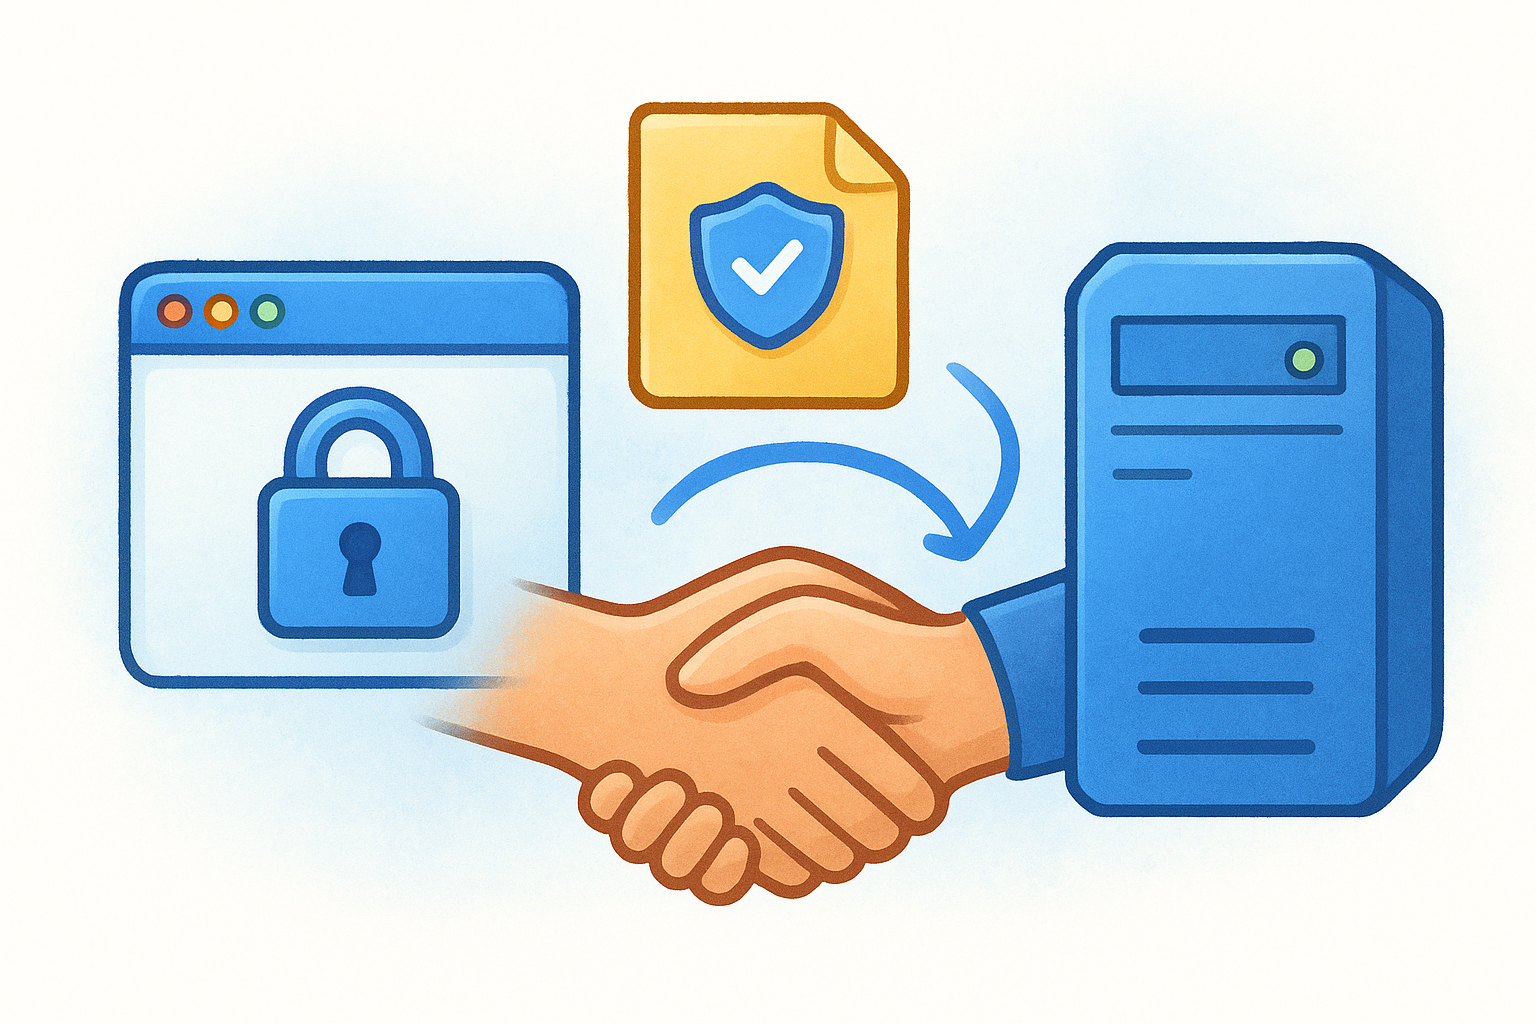
Your server decrypts this session key using its private key, and both sides now share the same secret key for encrypting and decrypting data during the visit. This initial exchange, called the SSL handshake, completes in under a second. The beauty of this system lies in the fact that only your server possesses the private key needed to decrypt that session key, meaning anyone intercepting the connection gets nothing but scrambled, useless data.
Encryption keeps data unreadable during transit
Once the handshake completes, every piece of information traveling between the browser and your server gets scrambled using that session key. Credit card numbers become random strings of characters, passwords transform into gibberish, and contact forms turn unreadable to anyone monitoring the network traffic. The encryption algorithm uses complex mathematical formulas that make it computationally impossible for hackers to reverse the process without the decryption key.
Your SSL certificate creates a secure tunnel where data remains encrypted even if someone intercepts the connection, protecting your customers from identity theft and data breaches.
This protection extends to every interaction on your site, from simple page loads to checkout processes, ensuring complete privacy for your visitors throughout their entire browsing session.
SSL certificate types and which one to choose
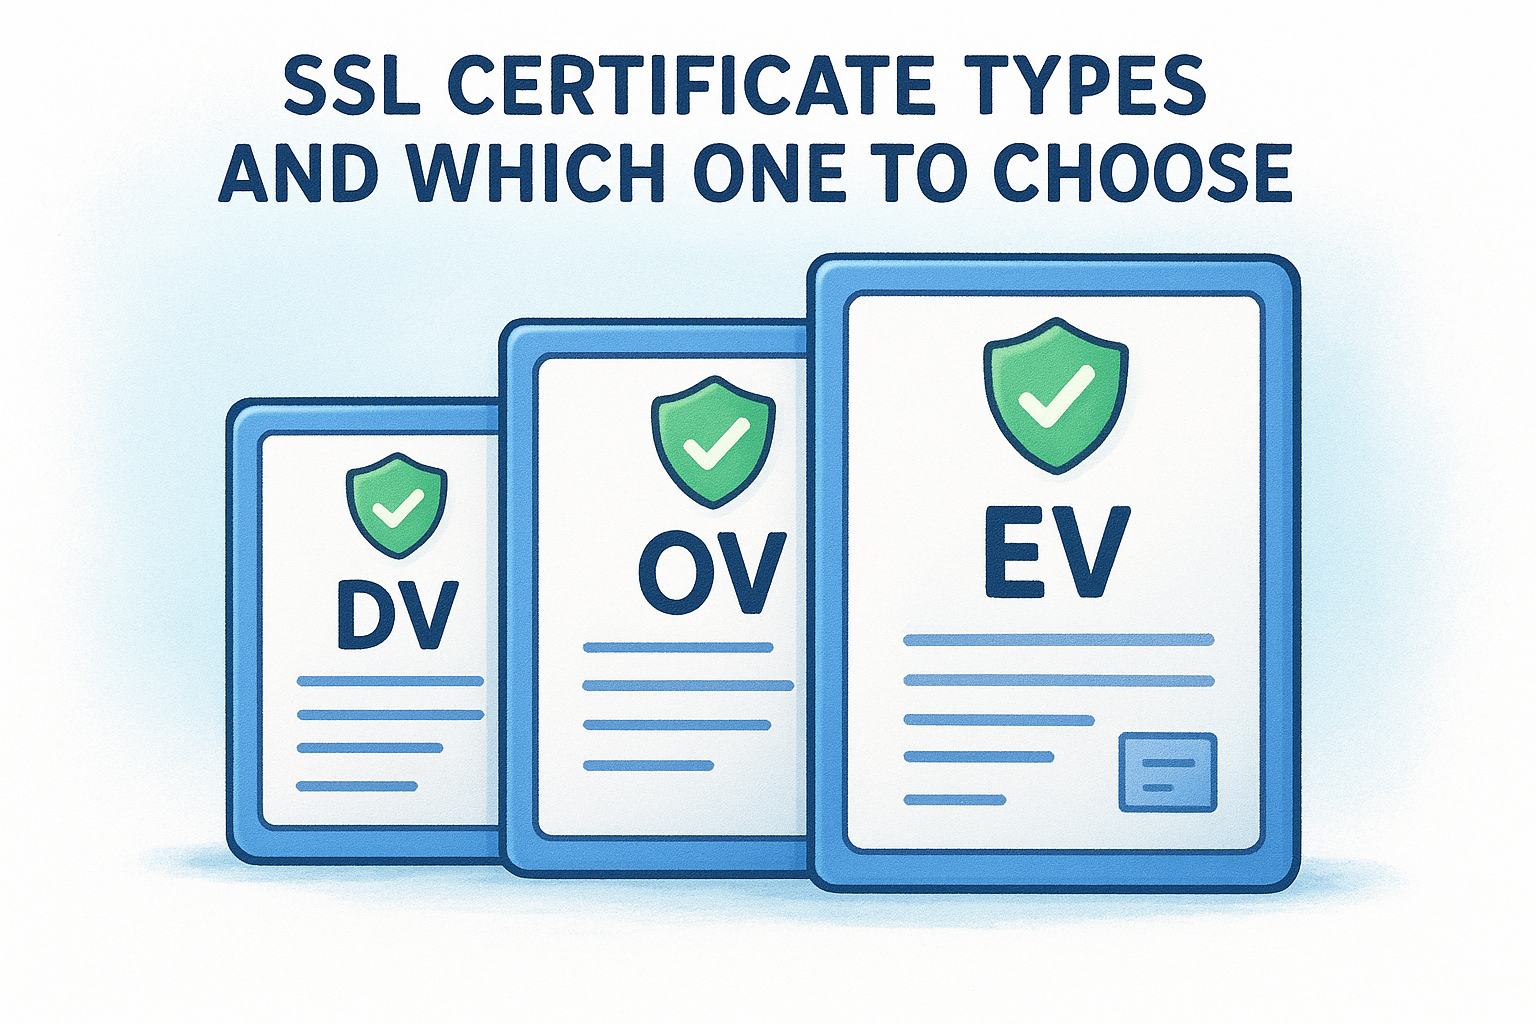
Certificate Authorities offer three main types of SSL certificates, each with different validation levels and trust indicators. Choosing the right one depends on your business size, budget, and how much identity verification your customers need to see. Understanding what is an ssl certificate includes knowing these distinctions, because the wrong choice either wastes money on unnecessary validation or fails to provide adequate trust signals for your specific business needs.
Domain Validated (DV) certificates
DV certificates represent the most basic SSL option and verify only that you control the domain name. The Certificate Authority sends an email to your domain’s registered contact or checks for a specific DNS record, confirming ownership in minutes. These certificates cost between $0 and $50 annually (Let’s Encrypt offers them free) and work perfectly for blogs, portfolios, and small informational websites where you’re not collecting sensitive customer data or processing payments.
Organization Validated (OV) certificates
OV certificates add a business verification layer where the Certificate Authority confirms your company legally exists by checking business registration documents. This validation process takes 1-3 business days and costs $50-$200 annually, but the certificate displays your verified company name when visitors click the padlock icon. Small businesses handling customer information or running e-commerce sites gain credibility through this extra verification, which reassures customers they’re dealing with a legitimate registered business rather than a potential scam site.
Extended Validation (EV) certificates
EV certificates provide the highest level of validation through rigorous background checks including legal existence, physical address, and phone verification. These certificates previously displayed your company name directly in the address bar (browsers removed this feature in 2019), but they still show extensive organization details when users inspect the certificate. The $200-$1,000 annual cost makes sense primarily for large e-commerce operations, financial institutions, and businesses where customer trust directly impacts high-value transactions.
Most small businesses get everything they need from a free DV certificate or a moderately-priced OV certificate, making EV certificates unnecessary unless you’re processing substantial transaction volumes.
Which certificate type fits your business
Match your certificate choice to your actual business requirements rather than buying more validation than necessary. Basic service websites, local businesses, and content sites perform perfectly well with DV certificates, while online stores and service providers collecting customer information benefit from OV certificates that verify your business legitimacy. Reserve EV certificates for situations where your business model depends on displaying maximum trust signals to customers making significant purchasing decisions.
How to get, install, and renew an SSL certificate
Getting an SSL certificate installed on your website sounds technical, but most hosting providers handle the heavy lifting for you. Understanding what is an ssl certificate includes knowing the practical steps to implement one, which typically takes less than 30 minutes from start to finish. Your exact process depends on whether you’re using managed hosting (where your provider does most of the work) or managing your own server (where you handle installation yourself).
Getting your certificate from your hosting provider
Most modern hosting companies include free SSL certificates through Let’s Encrypt or similar providers as part of your hosting package. Log into your hosting control panel and look for an SSL or security section where you’ll find a button to activate SSL for your domain. The system automatically generates the certificate, validates your domain ownership, and installs it on your server within minutes. Hosts like Bluehost, SiteGround, and HostGator all offer one-click SSL activation that requires zero technical knowledge.
If your host doesn’t provide free certificates, you’ll need to purchase one separately from Certificate Authorities like DigiCert or Sectigo, then upload the certificate files through your hosting control panel. This process involves downloading certificate files, pasting them into specific fields in your hosting dashboard, and verifying the installation completed correctly.
Configuring HTTPS and checking your installation
After installing the certificate, you need to force all traffic to HTTPS by adding redirect rules that automatically send visitors to the secure version of your site. Your hosting control panel usually includes an option to enable HTTPS redirection with a single toggle switch. Test your installation by visiting your site with "https://" in the address bar and checking for the padlock icon without any warnings.
SSL certificates expire every 90 days (for free certificates) or annually (for paid certificates), making automatic renewal critical to avoid sudden security warnings that drive visitors away.
Most hosting providers automatically renew Let’s Encrypt certificates before they expire, but you should verify this feature is enabled in your hosting settings and monitor renewal emails to catch any failures before they impact your site.
Next steps for securing your website
You now understand what is an ssl certificate, how encryption protects your visitors, and which certificate type fits your business needs. The implementation process is straightforward: check if your hosting provider offers free SSL certificates, activate them through your control panel, and configure HTTPS redirection to force secure connections across your entire site. Most small businesses complete this setup in under 30 minutes.
Your website’s security extends beyond just installing an SSL certificate. Regular software updates, strong passwords, and reliable backups work together to create comprehensive protection for your online presence. At Avatar Website Design, we build websites with SSL implementation included from day one, handling all technical details so you focus on running your business rather than troubleshooting security warnings. Our maintenance plans keep your certificate renewed, your site updated, and your customer data protected without requiring any technical knowledge on your part.