

Your WordPress site is a target. Not because you’re special, because WordPress powers over 40% of the web, and attackers love low-hanging fruit. A WordPress security hardening service takes your site from "easy prey" to "not worth the trouble" by locking down every layer, from file permissions to login protocols. If you’ve been putting this off, 2026 is the year to stop gambling with your business website.
Small businesses get hit the hardest. You probably don’t have a dedicated IT team watching your site around the clock, and hackers know that. They use automated bots that scan thousands of WordPress installations per hour, looking for outdated plugins, weak passwords, and default configurations. One breach can tank your search rankings, expose customer data, and cost you weeks of recovery time. The financial and reputational damage is rarely something a small business can shrug off.
At Avatar Website Design, we build and maintain WordPress sites for small businesses every day, and security hardening is baked into how we work. We’ve seen what happens when it’s neglected, and we’ve seen how straightforward proper hardening can be when you know what to prioritize. This guide breaks down exactly what a professional WordPress security hardening service covers in 2026, what the process looks like, and how to evaluate whether you need outside help or can handle it yourself. Let’s get into it.
What a WordPress hardening service includes in 2026
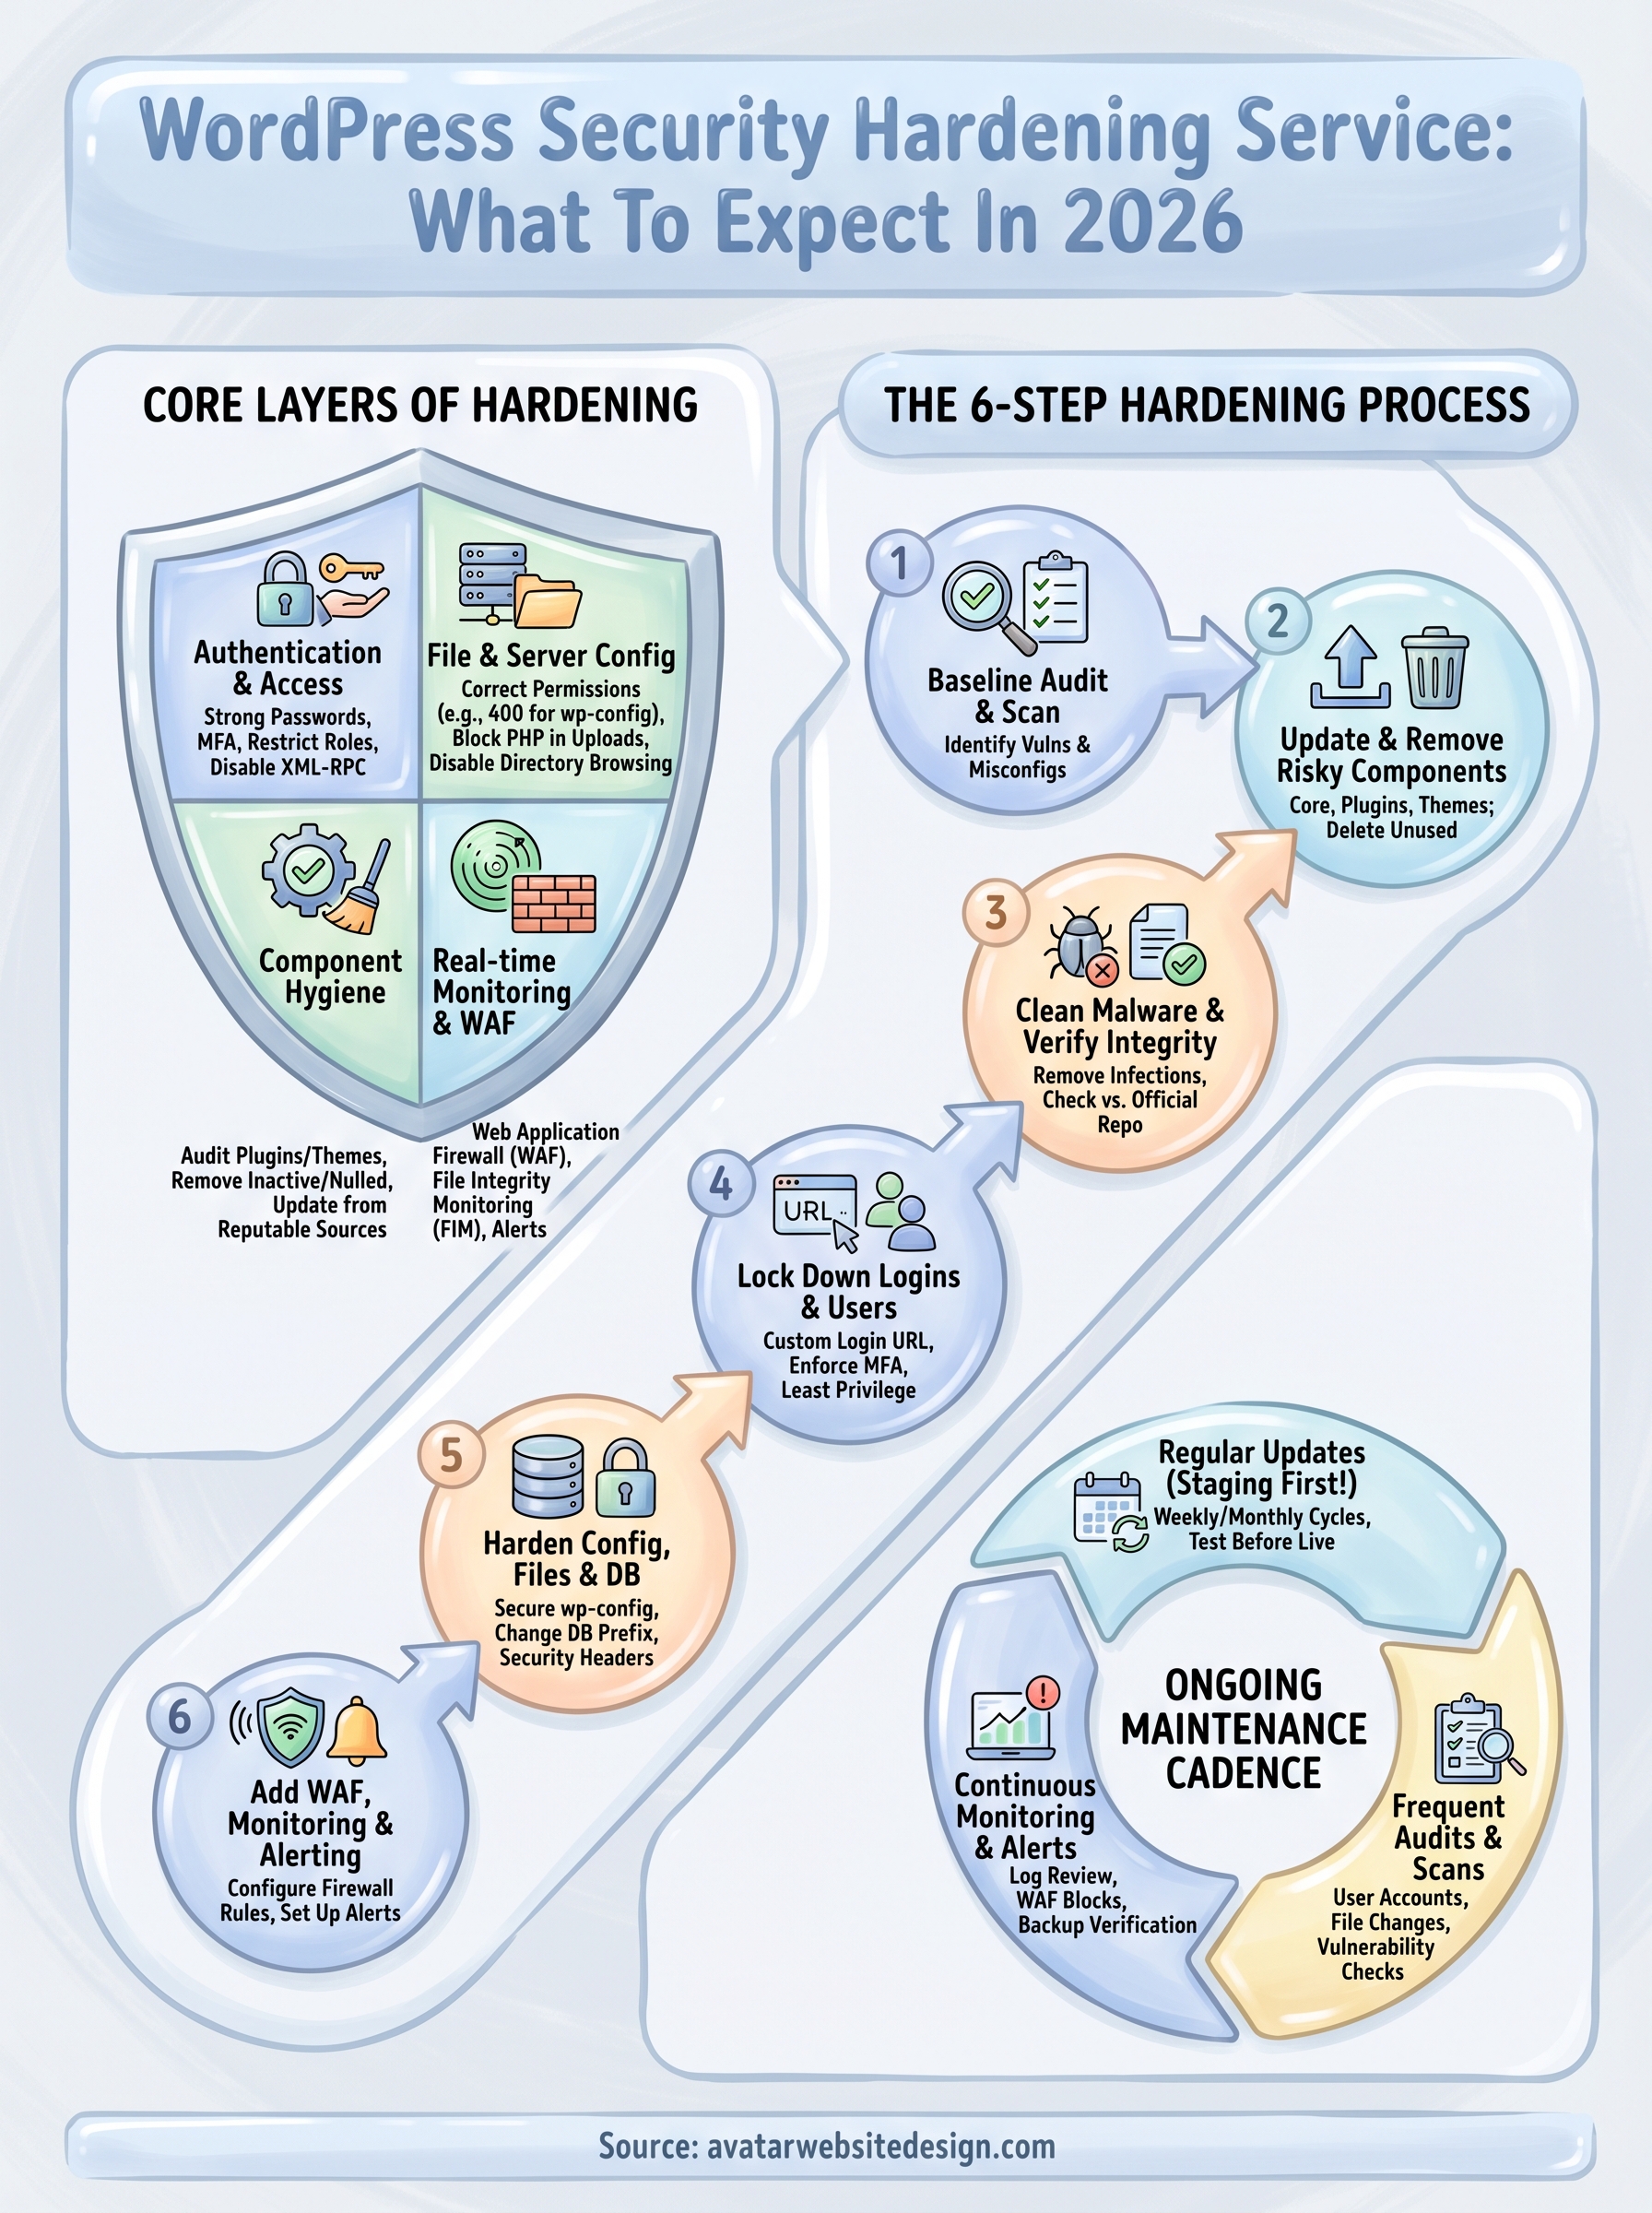
A modern WordPress security hardening service covers far more than installing a security plugin and calling it done. In 2026, the threat landscape demands a layered approach that addresses authentication, file integrity, server configuration, and real-time monitoring. Providers typically scope their work across six to eight distinct layers, each targeting a different attack surface on your site.
Authentication and access controls
Weak logins remain the number one entry point for attackers. A hardening service enforces strong password policies and multi-factor authentication (MFA) for every admin account on your site. Beyond that, providers audit your user list, remove dormant accounts, and restrict role permissions so editors can’t accidentally change critical settings.
Common authentication hardening tasks include:
- Changing the default
/wp-adminlogin URL to something unpredictable - Limiting login attempts to block brute-force bots
- Enforcing MFA via an authenticator app
- Disabling XML-RPC if you don’t use it (a frequent brute-force target)
- Removing the "admin" username if it still exists on your installation
Disabling XML-RPC alone can stop a significant percentage of automated brute-force attacks that target WordPress sites daily.
File permissions and server configuration
Attackers who get past your login screen go straight for your files. Correct file permissions prevent unauthorized writes to your core WordPress files, themes, and plugins. A hardening service sets wp-config.php to 400 or 440, locks down the wp-content directory, and blocks direct PHP execution in folders like /uploads where uploaded files live.
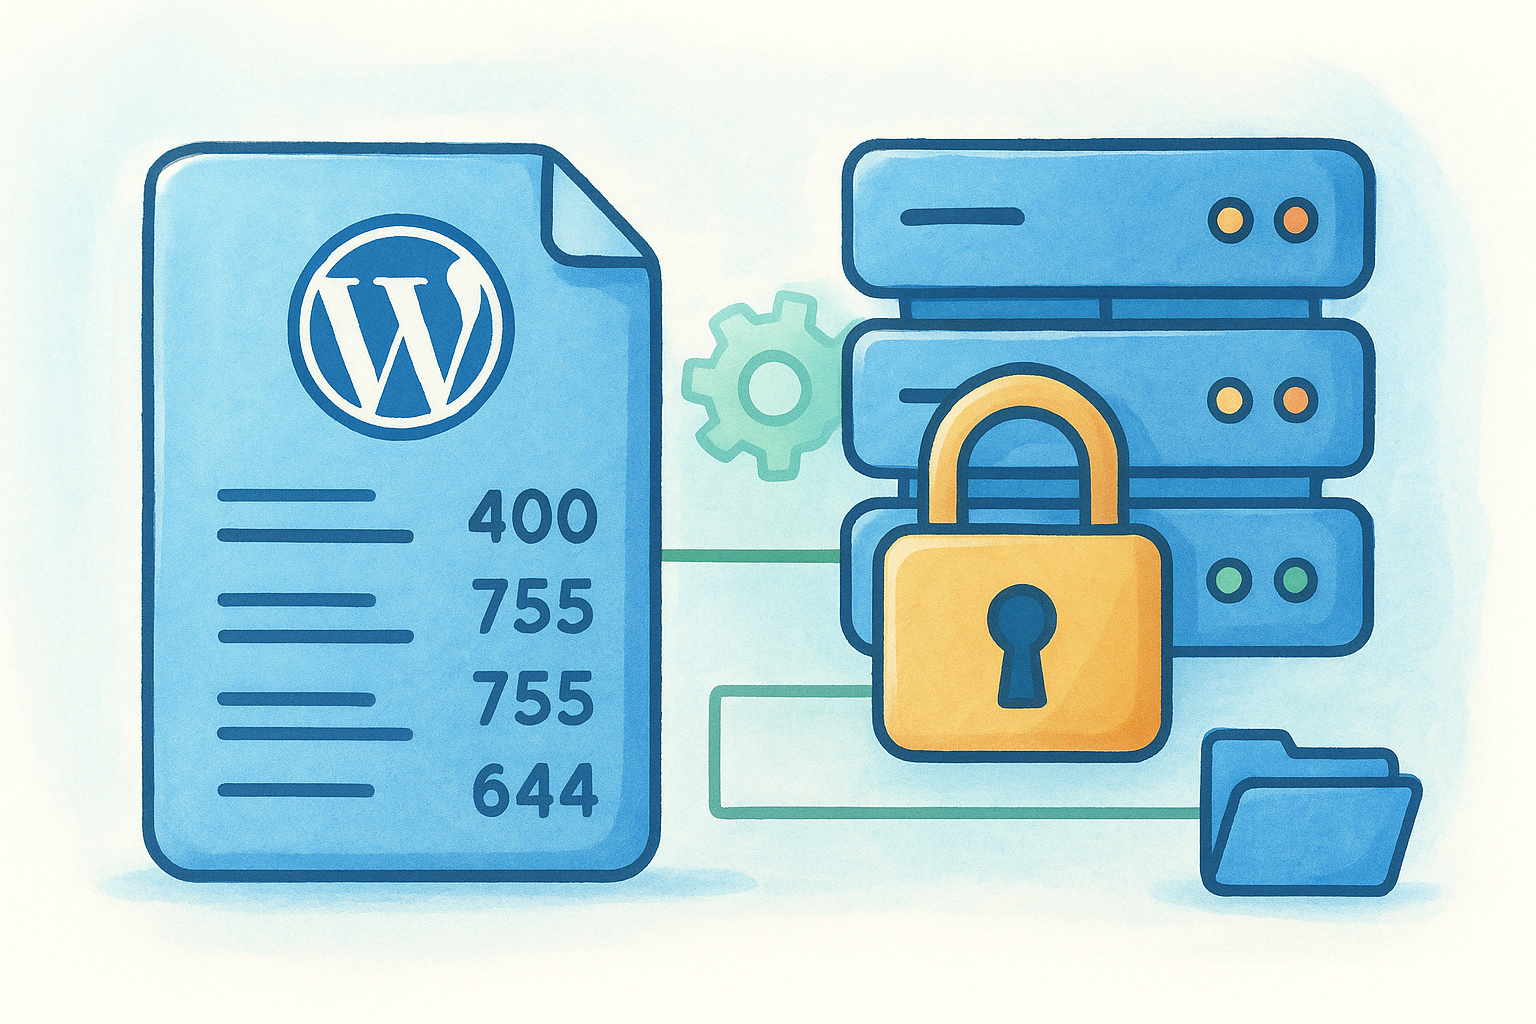
Here’s what properly hardened file permissions look like:
/wp-config.php        400 (owner read only)
/wp-content/          755
/wp-content/uploads/  755 (PHP execution blocked via .htaccess)
/.htaccess            444
WordPress core files  644
Providers also disable directory browsing through .htaccess so visitors and bots can’t list files in your directories and map your entire site structure.
Plugin, theme, and core software hygiene
Your installed components are one of the largest attack surfaces on any WordPress site. A hardening service audits every installed plugin and theme, removes anything inactive or abandoned, and verifies that all remaining components are current and sourced from reputable repositories. Abandoned plugins with no updates in over 12 months get flagged for replacement.
Providers also check for:
- Nulled (pirated) themes or plugins that often carry hidden malware payloads
- Plugins with known, unpatched CVEs listed in public vulnerability databases
- Redundant plugins doing jobs that WordPress handles natively
Real-time monitoring and WAF setup
No hardening effort is complete without ongoing visibility into what’s hitting your site. A web application firewall (WAF) sits in front of your WordPress installation and filters malicious traffic before it ever reaches your server. File integrity monitoring alerts you the moment a core file changes, which is one of the fastest ways to catch a compromise early.
Most services in 2026 pair a WAF with automated malware scanning, uptime monitoring, and log review. Together, these layers mean that even if something slips through, you’ll know about it within minutes rather than weeks. That speed is the difference between a quick file restoration and a full site rebuild.
How to choose the right provider and scope
Not every WordPress security hardening service is built the same way. Some providers offer a one-time checklist-based audit that checks boxes without understanding your specific stack. Others build a custom scope around your site’s size, plugins, hosting environment, and risk profile. Choosing the right fit starts with knowing what questions to ask before you hand over admin credentials.
What to look for in a provider
Your provider should demonstrate verifiable experience with WordPress specifically, not just general web security. Ask them for a sample audit report or a breakdown of their methodology. If they can’t explain what they check, in plain language, that’s a red flag. Look for providers who are familiar with common CVE databases like the National Vulnerability Database and who reference specific WordPress vulnerabilities by name rather than vague concepts.
Use this checklist when evaluating providers:
- Can they show you a sample deliverable or post-hardening report?
- Do they offer a staging environment for testing changes before applying them to your live site?
- Do they explain what they will and will not touch on your server?
- Is malware removal included, or is it a separate line item?
- Do they offer ongoing monitoring after the initial hardening, or is it a one-time engagement?
- Are they transparent about which tools and methods they use?
A provider who refuses to share their process or sample reports is not someone you want touching your production environment.
Defining the scope before you sign
Scope creep is one of the biggest sources of friction in security engagements. Before any work begins, get the full scope in writing with a clear list of deliverables. A solid scope document specifies which WordPress installation is covered, whether subdomains or staging environments are included, and exactly which hardening steps are in and out of scope.
Here is a basic scope template you can use to align expectations with any provider:
Site URL(s):
Hosting environment (shared / VPS / managed):
Includes malware scan and removal: Yes / No
Includes WAF setup: Yes / No
Includes login hardening: Yes / No
Includes file permission review: Yes / No
Includes post-delivery monitoring: Yes / No
Deliverable format (written report / video walkthrough / both):
Timeline:
Filling this out before your first call keeps both sides accountable and prevents billing surprises when the engagement wraps up.
Before kickoff: access, backups, and staging
Before any WordPress security hardening service provider touches a single file, three things need to be in place: the right access credentials, a verified backup, and a staging environment to test changes safely. Skipping any of these steps puts your live site at risk, and a good provider will ask for all three before they start. This prep work takes roughly an hour but can save you days of recovery time if something goes wrong mid-engagement.
What access to provide
Your provider needs specific, limited credentials rather than your master hosting account password. Create a temporary admin user in WordPress with a strong, unique password and share that alongside SFTP credentials for file-level access. Some hardening tasks require server-level changes, so confirm with your provider exactly what access they need before the engagement begins. Revoke every credential the moment the work is complete.
Here’s a pre-kickoff access checklist:
- WordPress admin account (temporary, removed after work completes)
- SFTP or SSH credentials for file access
- Hosting control panel access (only if server configuration changes are in scope)
- DNS access (only if WAF setup requires DNS record changes)
Never share your master hosting account login. Always create scoped, temporary credentials and revoke them as soon as the engagement ends.
Back up before anything changes
A verified full-site backup is non-negotiable before any hardening work begins. That means both your database and all site files. If your host provides automated backups, confirm the most recent backup completed successfully and download a local copy yourself rather than trusting a remote snapshot you can’t verify. Restore it to a test environment to confirm the files are intact and the site actually loads.
Your backup should include:
- Full database export (.sql file)
- All WordPress files, including
/wp-contentandwp-config.php - A clear timestamp so you know exactly which state you’re restoring to
Set up a staging environment
Applying hardening changes directly to your production site introduces unnecessary risk. A staging environment lets your provider test every configuration change against a live copy of your site without affecting real visitors. Most managed WordPress hosts include one-click staging. If yours does not, your provider should set one up on a subdomain before any work starts.
Once staging is ready, all changes get applied and verified there first, including login restrictions, file permission updates, and WAF rules. Only after a clean review does your provider migrate the finalized configuration to your live site.
Step 1. Run a baseline audit and vulnerability scan
The first thing any WordPress security hardening service does is take stock of exactly where your site stands before touching a single setting. Without a baseline audit, providers are guessing. A thorough scan surfaces every known vulnerability, misconfiguration, and outdated component so the hardening work that follows is targeted rather than generic.
What a baseline audit covers
Your provider runs automated and manual checks across four main areas of your WordPress installation. Automated tools cross-reference your installed plugin and theme versions against known vulnerability databases to flag anything with a published CVE. The manual review looks at things automated scans miss, including user account configurations, file permission structures, and server response headers that reveal too much about your environment.
A complete baseline audit checks:
- WordPress core version and available updates
- All installed plugins and themes (active and inactive) compared against vulnerability records
- File permissions on
wp-config.php,.htaccess, and the/wp-contentdirectory - User accounts, including role assignments and dormant admin accounts
- Server headers that expose version information such as PHP, Apache, or Nginx
- Login configuration, including whether XML-RPC and the REST API are open to the public
- Database table prefix (the default
wp_prefix is a known risk and should be changed)
Inactive plugins carry the same vulnerability risk as active ones. Anything installed on your site is part of your attack surface, even if it is turned off.
How to read the scan results
Your provider should deliver the audit findings as a prioritized list organized by severity, not a raw dump of scanner output. Critical findings, such as an actively exploited plugin vulnerability or a publicly accessible sensitive file, need to be resolved before anything else moves forward. Medium and low severity findings get addressed in subsequent hardening steps so nothing falls through the cracks.
A well-structured audit report maps each finding to a recommended fix and an estimated effort level. If your provider hands you a report without that context, ask them to add it. You need to understand what each finding means for your specific site and why it is being addressed in a particular order. That clarity also gives you a benchmark to measure against once hardening is complete, so you can confirm the work actually closed the gaps the audit identified.
Step 2. Update WordPress and remove risky components
Once your baseline audit is complete, your provider moves into the most straightforward but highest-impact phase of any WordPress security hardening service: updating every component and stripping out anything that poses unnecessary risk. Outdated software is responsible for the majority of successful WordPress breaches, so this step closes the gap between where your site is and where it needs to be before any deeper hardening begins.
Update everything in the right order
Updates need to happen in a specific sequence to avoid breaking your site. Your provider starts with WordPress core, then moves to plugins, then themes. Updating core first ensures any compatibility dependencies resolve before individual components get touched. Running these updates on your staging environment first is essential, and your provider should push them to production only after confirming nothing breaks.
Always update on staging before production. A plugin update that conflicts with your theme can take your entire site offline in under a minute.
Here is the correct update sequence to follow:
- WordPress core (check the WordPress.org download archive for the current stable release)
- Plugins (active first, then inactive)
- Themes (active theme first, then parent or child themes)
- PHP version (coordinate with your host to match your plugin compatibility requirements)
After updates complete, your provider verifies the site loads correctly on staging and runs a quick functional check across your key pages before migrating to the live environment.
Remove plugins, themes, and users you no longer need
Your provider then audits everything installed on your site and removes anything that does not serve an active, necessary purpose. Every inactive plugin and unused theme is an entry point that gets skipped during routine maintenance in practice, even if the intent is to update it eventually. Deletion is the only reliable fix.
Components flagged for removal include:
- Inactive plugins not used in the last 60 days
- Abandoned plugins with no developer updates in over 12 months
- Nulled or pirated themes and plugins, which frequently carry hidden malware payloads
- Duplicate plugins doing the same job, such as two separate contact form tools running simultaneously
- Dormant admin and editor accounts belonging to former contractors or employees
Reducing your installed component count directly reduces your attack surface, and that math is straightforward: fewer plugins means fewer potential vulnerabilities for automated scanners to find and exploit against your site.
Step 3. Clean malware and verify core file integrity
Even a site that looks healthy on the surface can be running malicious code injected weeks or months before you noticed anything wrong. This step is where your WordPress security hardening service provider moves from prevention into active remediation, scanning every file for known malware signatures, backdoors, and unauthorized code injections, then cross-checking your WordPress installation against the original files from the official WordPress.org repository.
How malware scanning and removal works
Your provider runs a file-level malware scanner across your entire installation, including /wp-content, /wp-includes, and /wp-admin. The scanner compares each file against known malware signature databases and flags anything that matches. Beyond automated signatures, your provider manually reviews suspicious files flagged for unexpected outbound connections, base64-encoded payloads, or eval() functions that attackers use to hide executable code inside otherwise ordinary-looking PHP files.
A site can look fully functional to visitors while running a spam mailer, redirecting mobile users to phishing pages, or silently harvesting form data in the background.
Confirmed malware gets removed, not quarantined. Your provider replaces infected files with clean versions pulled from a verified source and documents every change made during the cleanup so you have a clear record.
Verify core file integrity against the official repository
After cleanup, your provider verifies that every WordPress core file matches the official release. WordPress publishes cryptographic checksums for every core file in every release version, and diffing your installation against those checksums reveals any file that was added, modified, or deleted outside of a normal update process.
Here is the WP-CLI command your provider uses to run that integrity check:
wp core verify-checksums
Any file that fails the checksum check gets replaced with the official version pulled directly from WordPress.org. Your provider also checks for files that should not exist inside core directories at all, such as PHP shells or unfamiliar .php files sitting in /wp-includes or root-level directories. Those get deleted immediately.
Confirm clean state before moving forward
Once scanning and file replacement are complete, your provider runs a second scan to confirm no malware remains before proceeding to the next hardening step. Proceeding without a clean bill of health at this stage means layering new security controls on top of an already-compromised installation, which renders every subsequent hardening step unreliable. A documented clean-state confirmation is a standard deliverable you should expect at the end of this phase.
Step 4. Lock down logins, users, and admin permissions
With clean files and updated components in place, your WordPress security hardening service provider turns attention to access controls. Login pages and user accounts are the most actively targeted attack surface on any WordPress installation, with bots running thousands of credential attempts per hour against unprotected sites. Locking this layer down stops the majority of unauthorized access attempts before they ever reach your database.
Harden the login page and authentication
Your provider starts by changing the default /wp-admin login URL to a custom path that automated scanners cannot guess. Combined with enforced multi-factor authentication (MFA) for all admin accounts, this single change eliminates a large percentage of brute-force traffic. Login attempt limits get configured to block any IP address that fails authentication more than three to five times within a short window.
Relocating your login URL does not replace MFA. Apply both together so that attackers who find the new URL still face a second barrier they cannot easily bypass.
Here is the .htaccess block your provider uses to restrict direct access to the default login path on Apache servers:
# Restrict wp-login.php to authorized IPs only
<Files wp-login.php>
  Order Deny,Allow
  Deny from all
  Allow from YOUR.OFFICE.IP.ADDRESS
</Files>
XML-RPC also gets disabled unless your site specifically requires it for an active integration, since it remains one of the most exploited endpoints on unprotected WordPress installations. The REST API gets restricted to authenticated requests only where your site configuration allows that setting without breaking existing functionality.
Audit users and restrict permissions
Every user account on your site is a potential entry point, so your provider audits the full user list and removes or reassigns any account that no longer serves an active purpose. Former contractors, stale test accounts, and any account still using the username "admin" get deleted or renamed immediately.
Your provider then applies the principle of least privilege across all remaining accounts using this role assignment framework:
| Role | What they can do | When to use it |
|---|---|---|
| Administrator | Full site access | Site owner only |
| Editor | Publish and manage all posts | Content managers |
| Author | Publish their own posts only | Individual contributors |
| Contributor | Write but not publish | Guest writers |
| Subscriber | Read-only access | Members or customers |
No account should hold a higher role than the tasks that account actually performs. Reducing privilege levels across your user base limits the damage any single compromised account can cause if an attacker gets in.
Step 5. Harden configuration, files, and the database
With user accounts locked down, your WordPress security hardening service provider moves into the configuration layer. This step targets three areas that attackers exploit once they get past authentication: your wp-config.php file, server response headers, and database settings. None of these require exotic tools, but each one closes a specific gap that stays open on most default WordPress installations and gets overlooked during routine maintenance.
Lock down wp-config.php and server headers
Your wp-config.php file contains your database credentials, secret keys, and table prefix, making it the most sensitive file on your entire WordPress installation. Your provider moves it one directory above your web root, which prevents direct HTTP access, and sets its file permissions to 400 so only the server owner can read it. They also add a direct HTTP block inside your .htaccess file as a second line of defense against any request that targets the file directly.
Here is the .htaccess rule that blocks direct browser requests to wp-config.php:
<Files wp-config.php>
  Order Allow,Deny
  Deny from all
</Files>
Blocking
wp-config.phpat the server level ensures that even if a misconfiguration exposes your web root, your database credentials stay out of reach.
Your provider also adds security-focused HTTP response headers that instruct browsers to enforce strict content policies and block clickjacking attempts. These headers get added either through .htaccess on Apache or your nginx.conf on Nginx. Implementing them costs nothing and meaningfully reduces your exposure to cross-site scripting and content injection attacks that target unprotected WordPress front ends.
Harden the database
Default WordPress database settings are a documented risk, and your provider addresses the most critical ones directly. First, the default wp_ table prefix gets renamed to a randomized string, which neutralizes a large category of automated SQL injection payloads that hard-code the standard prefix. Second, your provider removes unused database user accounts and revokes excess privileges from the WordPress database user so it holds only the permissions WordPress actually needs to operate.
The WordPress database user requires only these privileges to function correctly:
- SELECT
- INSERT
- UPDATE
- DELETE
- CREATE
- DROP
- INDEX
- ALTER
Revoking everything beyond this list limits the blast radius of any attack that reaches your database through a vulnerable plugin. An attacker with a restricted database user cannot export your full database, create new admin accounts through SQL, or modify tables outside the scope of normal WordPress operations.
Step 6. Add a WAF, monitoring, and alerting
Every preceding step in a WordPress security hardening service reduces your exposure, but no configuration is perfectly attack-proof. A web application firewall (WAF) and real-time monitoring layer give you active protection and immediate notification when something suspicious happens, so you can respond before a small incident becomes a full site compromise. This step transforms your site from a static hardened target into one that actively defends itself and reports threats as they occur.
Set up your web application firewall
Your provider configures a WAF at the DNS level or directly on your server, depending on your hosting environment. A DNS-level WAF routes all traffic through a filtering proxy before it reaches your site, which stops malicious requests without adding load to your server. Server-level WAFs work at the application layer and integrate tightly with WordPress. Both approaches block common attack patterns, including SQL injection, cross-site scripting (XSS), and remote file inclusion attempts.
A WAF does not replace file permissions and login hardening. It filters traffic that reaches your site, while hardening reduces what attackers can do if a request gets through.
Your provider configures the WAF ruleset using a baseline that covers the OWASP Top 10 attack categories, then tunes the rules to avoid false positives on your specific forms, plugins, and admin workflows. Here is an example .htaccess rule that blocks common SQL injection patterns at the server level before a WAF plugin processes the request:
# Block common SQL injection patterns
RewriteCond %{QUERY_STRING} (\%27)|(\')|(\-\-)|(\%23)|(#) [NC]
RewriteRule .* - [F,L]
Configure file integrity monitoring and alerts
File integrity monitoring (FIM) compares your current WordPress files against a known-clean baseline and fires an alert the moment any file changes outside a scheduled update window. Your provider sets up automated scans on a daily schedule and configures alerts to reach you by email or SMS within minutes of a detected change. Most compromises leave traces in core files first, so catching a modified file early often stops an attack before it spreads to your database or customer data.
Your alert configuration should cover these specific trigger conditions:
- Any change to
wp-config.phpor.htaccess - New
.phpfiles appearing in/wp-content/uploads - Any modification to files inside
/wp-includesor/wp-admin - Failed login spikes exceeding 10 attempts within five minutes from a single IP
After delivery: maintenance and monitoring cadence
A completed WordPress security hardening service is not a finish line, it is a starting point. New vulnerabilities get published in plugin and theme repositories every week, and the hardened configuration your provider delivered on day one starts drifting the moment you install a new plugin or your host updates a server dependency. Ongoing maintenance and a defined monitoring cadence are what keep your site ahead of the threat rather than reacting to it after something breaks.
Set a recurring maintenance schedule
Consistent maintenance windows prevent the gradual configuration drift that turns a hardened site back into an easy target within months. Your provider should give you a documented cadence that specifies what gets reviewed, when, and who is responsible for each task. If you are managing maintenance yourself after the initial engagement, block time on a fixed schedule so it does not slide.
Use this cadence as your baseline:
| Frequency | Task |
|---|---|
| Weekly | Review security plugin logs and WAF block reports |
| Weekly | Confirm automated backups completed successfully |
| Monthly | Apply WordPress core, plugin, and theme updates on staging, then production |
| Monthly | Audit user accounts and remove any that are no longer active |
| Monthly | Review file integrity monitoring alerts and resolve any flagged changes |
| Quarterly | Run a full vulnerability scan against your current installed components |
| Quarterly | Rotate WordPress secret keys and database passwords |
| Annually | Full re-audit of your hardening configuration against current best practices |
Skipping your monthly update window even once creates a compounding risk, because attackers actively monitor CVE disclosures and begin targeting newly published vulnerabilities within hours of announcement.
What to track between scheduled reviews
Your monitoring tools generate signals between scheduled windows that require attention on a shorter timeline than monthly. Failed login spikes, new PHP files appearing in your uploads folder, and sudden changes in server response headers all warrant immediate investigation rather than waiting for your next calendar window. Set your alert thresholds low enough to catch anomalies early, but tune them carefully to avoid alert fatigue that causes you to start ignoring notifications.
Track these metrics on an ongoing basis:
- Failed login attempts per day (flag spikes above your rolling average)
- WAF blocks categorized by attack type to identify patterns
- Backup completion status and file size to catch corrupted or incomplete backups
- Uptime and page load time as indirect indicators of resource abuse or injected scripts
Taking Your Next Steps Toward WordPress Security
You now have a complete picture of what a professional wordpress security hardening service covers, from the baseline audit through ongoing maintenance cadence. Every step in this guide builds on the one before it, and skipping any layer leaves a gap that attackers are happy to exploit. The work is concrete, the tools exist, and the process is repeatable.
Start by running a baseline scan on your site this week using WP-CLI or a scanner like Wordfence. Document what you find, prioritize by severity, and work through each hardening step in the order outlined here. If your audit uncovers active malware, outdated plugins with known CVEs, or a configuration that needs more than a few hours to fix, that is a clear signal to bring in professional help.
Get expert help securing your WordPress site before the next automated bot scan finds your business first. Work with a team that builds and protects small business websites and handles the technical side so you can focus on running your business.